


Malicious indexed-btree npm package hid loader in runtime code
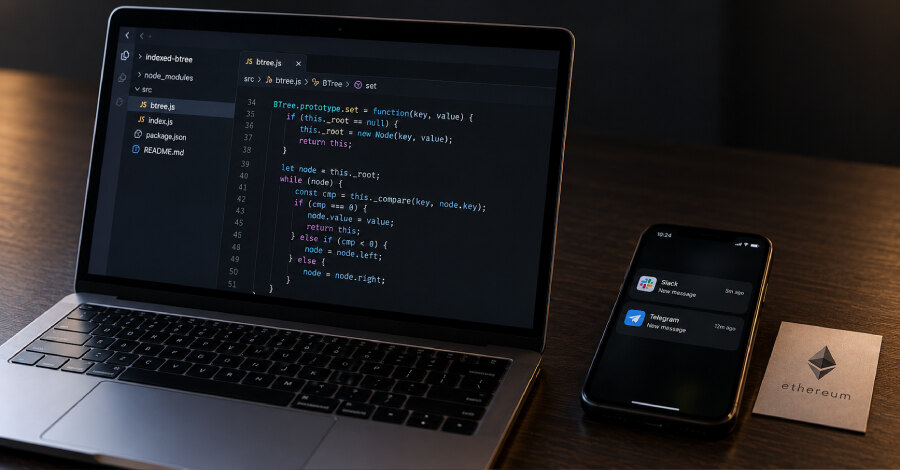
A malicious npm package named indexed-btree was removed from the npm registry after researchers found it concealed a malware loader in library runtime code rather than lifecycle scripts. Checkmarx said the package impersonated the legitimate sorted-btree B-tree and indexing utility. First uploaded on June 18, 2026, by the npm account charlessadler25, it accumulated millions of downloads in a short period and may have generated about €230,933.57, or 109 ETH, in cryptocurrency for its operator.
The technique is notable because npm version 12 introduced controls intended to prevent automatic execution of lifecycle scripts such as preinstall and postinstall. Those hooks are commonly used by legitimate packages for compilation, data seeding and configuration, but have also been a frequent path for supply-chain malware. Indexed-btree did not use either mechanism.
Loader embedded in a normal-looking method
Instead, Checkmarx found the loader inside the BTree.prototype.set() method. Calling that apparently ordinary library function triggered sharedLoad.min.js, a JavaScript payload containing an obfuscated first stage. The malware fingerprinted the host and beaconed collected details to a hard-coded Slack channel and Telegram bot.
It then used EtherHiding to retrieve encrypted next-stage blobs from a smart contract on the Sepolia testnet. The components were merged into a second-stage payload. The final routine deleted malicious artifacts and removed the trigger from the package code, an effort to conceal the activity after execution.
Controls must examine execution, not only installation
Checkmarx linked indexed-btree to an operation involving other npm packages that have also been removed, including ordered-kv-index, btree-leaderboard, priority-slot-queue, btree-range-store, btree-core, btree-time-index, btree-lru-cache, neighbor-key-map, sliding-score-window and mutex-forge.
The campaign illustrates a wider pattern in which attackers exploit trusted development channels, a risk reflected in trusted relationships as an attack path where familiar software relationships become an entry point. For npm users, blocking lifecycle scripts remains useful, but it cannot identify malicious code that waits for an application to invoke a legitimate-looking function.
Checkmarx recommends adding runtime behaviour analysis to install-time scanning and lifecycle-script controls. Ensar Seker, CISO at SOCRadar, said defenders need layered measures that detect malicious activity before installation, during execution and after deployment. Businesses should therefore assess dependencies for runtime network behaviour, host fingerprinting and staged-payload retrieval as part of their software supply-chain monitoring.
PolinRider activity also reaches Packagist
The disclosure coincided with Socket's removal of malicious code from the dev-main version of visanduma/nova-two-factor, a Packagist package with more than 700,000 cumulative downloads. Socket tied the incident to the North Korea-linked PolinRider campaign and said Visanduma GitHub repositories had been compromised since mid-June 2026 through the LaHiRu developer account.
Socket reported heavily obfuscated JavaScript inserted directly into index.php and launched through PHP's shell_exec(). It said the activity shows that package-registry compromise can stem from broader Git-based intrusions, allowing operators to use ordinary collaboration and release workflows as additional distribution paths. The practical implication is to monitor source repositories, developer environments and published packages as connected parts of the same exposure surface.