


NatJack flaws show how shared NAT state can be manipulated
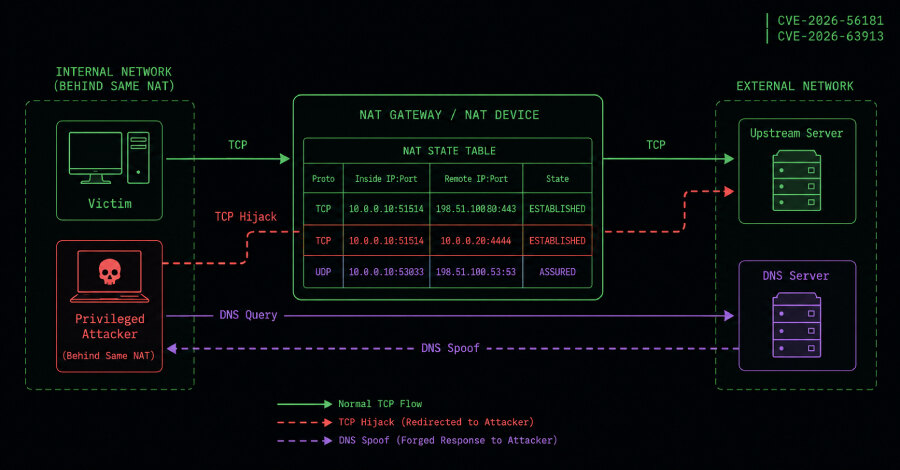
Security researcher Malcolm Stagg has disclosed NatJack, an attack class that manipulates network address translation connection state to hijack active TCP sessions, spoof DNS responses, expose mapped ports and exhaust NAT tables. Presented at Black Hat USA 2026, the research identified affected behavior in independently developed implementations, including Windows and Linux.
Two implementation-specific vulnerabilities have CVE assignments. CVE-2026-56181, with a CVSS score of 8.3, affects Windows NAT used by Hyper-V. CVE-2026-63913, rated 8.2, affects Linux Netfilter conntrack. NatJack generally requires an attacker to hold privileged access on a system behind the same NAT as the victim.
How NatJack changes connection state
Stagg conducted the work independently through SODIUM-24. It challenges the assumption in many NAT implementations that hosts sharing a NAT device cannot alter one another’s connection state. Depending on the implementation, a compromised host can manipulate connection-tracking entries associated with another internal system.
The research outlines four principal techniques. An attacker can replace a NAT mapping to redirect traffic from an active TCP connection. A second technique interferes with a victim DNS request, causing the legitimate response to reach the attacker and enabling a forged reply to be sent to the victim. Other methods can reveal externally mapped ports or fill the NAT connection table with spoofed flows, preventing legitimate clients from opening new connections.
Synack said Stagg tested the techniques against dozens of real-world network infrastructure products from multiple vendors and demonstrated proof-of-concept exploitation in a controlled environment. The NatJack site does not provide a full product-by-product matrix, and there was no public evidence of exploitation in the wild as of August 7, 2026.
Windows and Linux fixes address specific flaws
For Linux, the kernel.org CNA record says a crafted SYN followed by a reset packet with an invalid sequence number can prematurely place an active Netfilter NAT entry in a closed state because conntrack did not validate packet direction. Fixed stable releases are 5.10.259, 5.15.210, 6.1.176, 6.6.143, 6.12.93, 6.18.35, 7.0.12 and 7.1.
Stagg noted that the Linux kernel change fixes the code flaw but only mitigates the broader downstream-spoofing technique by making it more complex. Microsoft describes its issue as an origin-validation error enabling spoofing from an adjacent network. Affected versions include Windows 11 24H2 before 26100.8875, 25H2 before 26200.8875, 26H1 before 28000.2525, and Windows Server 2025 before 26100.33158.
Segmentation is the practical control
NatJack extends a line of NAT-state research that has already shown router exposure: Linux rootkits, router zero-day and AI attacks documented Linux rootkits, a router zero-day and AI attacks, while an NDSS 2024 study found 52 of 67 tested routers susceptible to its NAT-mapping TCP hijacking attack and resulted in ten CVEs.
There is no single patch for the broader NatJack class. Businesses should install available Windows and Linux updates, separate untrusted workloads from trusted systems that share NAT infrastructure, encrypt traffic inside internal networks and deploy IP Source Guard where applicable.