


Windows Hello for Business Keys Can Be Abused for Entra ID Persistence
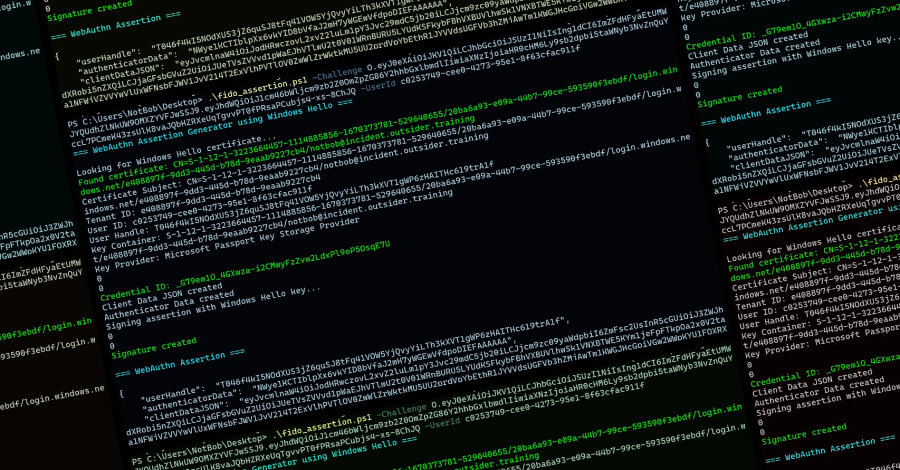
Windows Hello for Business keys can be invoked from a compromised session
Entra ID researcher Dirk-jan Mollema has demonstrated that malware already running in a user’s signed-in Windows session can silently invoke that user’s Windows Hello for Business key to authenticate to Microsoft Entra ID. The technique does not require administrator privileges, recovery of the user’s PIN, a biometric prompt, or extraction of a TPM-backed private key.
The attacker can use the authentication result to establish longer-term cloud access. In deployments where the relevant tenant policies allow it, the chain can include registering an attacker-controlled device, obtaining a Primary Refresh Token (PRT), and adding further authentication methods.
How the authentication chain works
Windows ticketing makes private-key operations available while the user is interactively signed in. Code executing as that user can therefore ask Windows to sign authentication data without exporting the key. Mollema describes this as a consequence of the Windows Hello for Business design, rather than a reported active exploitation case.
His earlier DEF CON 32 presentation in 2024 showed that a compromised session could produce a signed assertion for a PRT, but it required access to an Entra-registered or joined device. The newer work removes that prerequisite by treating the Windows Hello for Business key as a FIDO2 passkey through WebAuthn.
The researcher found that Entra ID’s five-minute challenge is not bound to a session, user, or tenant. An attacker can request the challenge from another host and have the compromised Windows endpoint produce the signed assertion. ROADtools can then use that assertion to request tokens or open a browser session as the victim.
Missing device binding can enable persistence
Mollema found that the resulting token carries no device ID claim. Without that binding, an attacker may register a new device, request a PRT for it, and access Microsoft cloud services. Microsoft states that a PRT remains valid for 90 days and is continuously renewed while the user actively uses the device.
The WebAuthn sign-in can also meet Conditional Access requirements for Microsoft’s phishing-resistant authentication strength and count as fresh multi-factor authentication. Where policy permits, that could allow the attacker to add passkeys or Windows Hello for Business keys on the newly registered device. The risk complements unauthorized Microsoft 365 access through Entra authentication flows because both scenarios examine paths to unauthorized Microsoft 365 access through Entra authentication flows.
Separate device-state or compliance requirements can interrupt the full sequence, so it will not work in every deployment. There were no reported victims, and searches of Microsoft’s Security Update Guide, NVD, and CVE.org found no related CVE or Microsoft advisory as of August 6, 2026. The disclosure also does not identify the Windows builds or Windows Hello for Business deployment models tested.
Detection focus for identity teams
Mollema recommends monitoring unexpected device registrations and hunting for Windows Hello for Business sign-ins with an empty device ID. Legitimate incognito or non-SSO browser sessions can show the same pattern, so that signal needs investigation rather than automatic attribution. Businesses should test whether their device-state and compliance controls prevent this persistence path after endpoint compromise, then review anomalous registrations and authentication-method changes.