


APT29 Uses Hijacked Analytics Scripts for Mobile Exploit Delivery
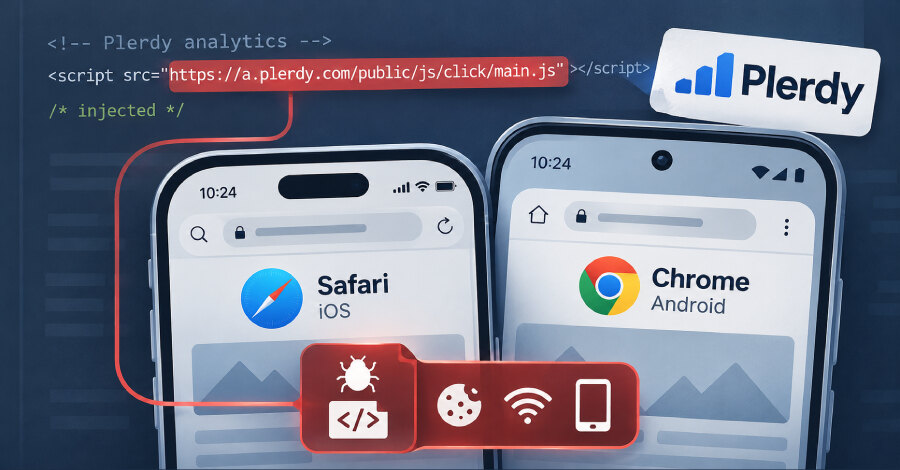
APT29-linked operators ran a large-scale watering-hole campaign that delivered iOS and Android exploit chains through compromised websites, lookalike domains and a supply-chain compromise of the Ukrainian analytics service Plerdy SEO Tracker. Sekoia discovered the activity, dubbed Poisoned Source, in mid-October 2026.
The Plerdy compromise lasted from August 27 to September 3, 2026. Attackers injected malicious code into a.plerdy[.]com/public/js/click/main.js, allowing sites that loaded the script to profile visitors and route them to platform-specific payloads.
Sekoia said the injected JavaScript gathered browser and device attributes before the delivery infrastructure selected an N-day exploit chain for iOS or Android. The stated objective was data theft: browser cookies in some cases, and Wi-Fi passwords or broader mobile-device data in others.
Three routes into the campaign
The operation used three infection vectors: malicious JavaScript injected into legitimate websites, lookalike sites posing as prominent organizations in the US, Ukraine, the Czech Republic and Bulgaria, and the compromised Plerdy SEO Tracker script. Identified compromised sites included a major US chemical-industry trade association, a far-right European political party and a Bulgarian military-related website.
Sekoia said it was unclear whether the operators focused on visitors to specific sites or attempted to compromise unpatched phones at scale before identifying information of interest. Several affected sites were likely to attract visitors of strategic value in the context of the Russia-Ukraine war, including military, special-forces and military-equipment audiences.
iOS and Android chains target different data
Class A targeted iOS 16.7 with CVE-2025-43529 and CVE-2024-27834, delivering JavaScript malware intended to steal cookies. Class B targeted iOS 18.5 with a DarkSword chain using CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510 and CVE-2025-43520.
The Class B payload could collect extensive device data, including SMS and iMessages, Apple Mail databases, voicemail, WhatsApp and Telegram databases, iCloud Keychain and Wi-Fi passwords, contacts, call history, Safari history and cookies, photos, and data from Apple Health, Calendar, Notes and iCloud Drive.
Class C targeted Chrome 139 through 145 on Android, excluding version 143, with CVE-2026-3910 and CVE-2025-27038. The chain aimed to obtain remote code execution, escape the sandbox and elevate privileges before delivering AndroSnitch, which collected Chrome data and Wi-Fi passwords. It stopped exploitation when it detected the Samsung Galaxy S25 Ultra model identifier SM-S938B.
All three chains sent exfiltrated data to the same telemetry endpoint. Sekoia also linked AndroSnitch to similarities with ANDROSNATCH, a Chrome cookie-stealing payload Google documented in August 2024 in a suspected APT29 watering-hole campaign.
What organisations should take from the incident
The case shows that externally hosted analytics code can become a route to mobile exploitation, not merely a privacy or website-integrity concern. Organisations should maintain an inventory of third-party scripts, review unexpected changes in hosted JavaScript, and ensure managed mobile browsers and operating systems receive security updates promptly. For security teams, web-tag governance and mobile patching belong in the same exposure-management conversation.