


CISA Sets Federal Deadlines for Exploited Plex, Siemens and SiteGuard Bugs
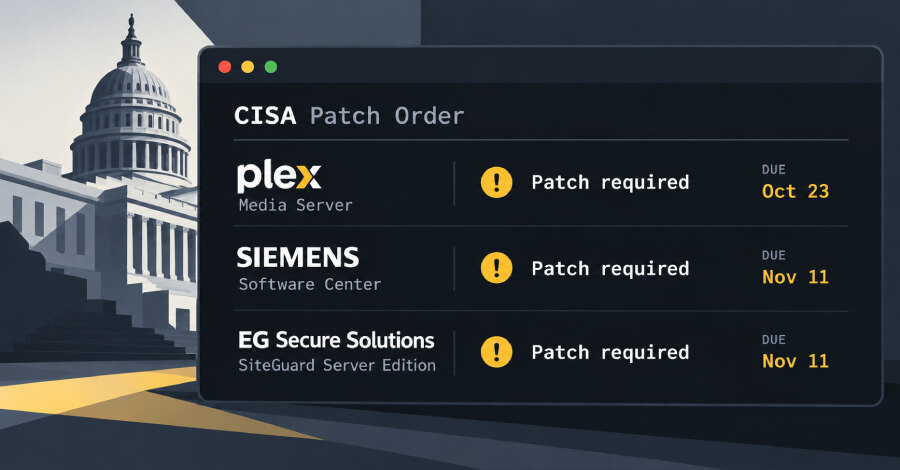
The U.S. Cybersecurity and Infrastructure Security Agency has added six actively exploited vulnerabilities to its Known Exploited Vulnerabilities catalog: four flaws in Plex Media Server collectively referred to as Plex2Shell, plus issues in Siemens Software Center and EG Secure Solutions SiteGuard Server Edition. Federal Civilian Executive Branch agencies have until October 23, 2026 to remediate three of the entries and until November 3 for the others.
The accelerated October 23 deadline applies to CVE-2026-106931 in SiteGuard Server Edition and the Plex Media Server flaws CVE-2026-96656 and CVE-2026-96654. CISA set November 3 as the remediation date for CVE-2026-96652, CVE-2026-96655 and CVE-2026-110936.
Plex2Shell chain enables unauthenticated code execution
The four Plex vulnerabilities were discovered and reported by security researcher Zach Main. They comprise two server-side request forgery issues, CVE-2026-96652 and CVE-2026-96655, each with a CVSS score of 5.3; CVE-2026-96654, an improper neutralization of encoded URI schemes in a web page, rated 6.9; and CVE-2026-96656, an external control of file name or path vulnerability rated 8.6.
Main said a remote attacker could chain the four weaknesses to obtain unauthenticated remote code execution. Plex addressed the issues in Plex Media Server 1.43.3.10861, released on August 3, 2026. Security researcher boredhackerblog reported that threat actors are weaponizing the flaws to deploy cryptocurrency miners and proxy malware.
Siemens and SiteGuard vulnerabilities are also exploited
CISA also added CVE-2026-110936, a CVSS 8.4 DLL sideloading vulnerability in Siemens Software Center. The flaw has been abused in ClickFix attacks using a platform called Romulus. The agency did not provide further technical detail on the observed activity.
The remaining entry, CVE-2026-106931, is a CVSS 8.5 command injection vulnerability in EG Secure Solutions SiteGuard Server Edition. The Japanese company confirmed that the issue is being exploited, although no additional information about that exploitation activity is available.
What organizations should do now
KEV inclusion signals that exploitation is active rather than theoretical. Organizations using Plex Media Server, Siemens Software Center, or SiteGuard Server Edition should identify affected deployments, verify whether Plex Media Server 1.43.3.10861 or applicable vendor fixes are installed, and treat the CISA remediation dates as a practical prioritization point for their own patch programs.