


FBI Announces Further Arrest in ShinyHunters Jobs Portal Case
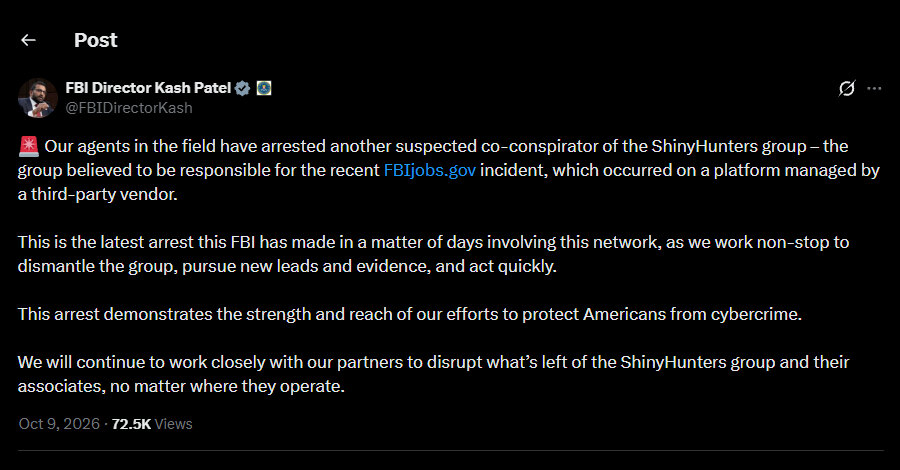
The FBI has announced another arrest in its investigation of ShinyHunters, the extortion group that claimed in September to have breached the FBIjobs.gov employment portal and stolen sensitive information on nearly all FBI agents and job applicants. FBI Director Kash Patel disclosed the action in an October 9 post on X, but neither the agency nor Patel named the suspect or published charges.
The New York Times and CBS News, citing unnamed sources, reported that the suspect is a Canadian citizen arrested in Pennsylvania. The Times said the arrest concerned suspected involvement in the theft of FBI data, while a law-enforcement source told CBS News the person was believed to have been directly involved in the intrusion. Patel’s statement did not specify whether the detainee participated in the breach.
Third publicly reported arrest
Reuters counted the Pennsylvania detention as the third arrest made public after news of the incident emerged in late September. Patel described ShinyHunters as the group believed responsible for the FBIjobs.gov incident and said the FBI would continue working with partners to disrupt remaining members and associates regardless of where they operate.
Earlier actions involved a 24-year-old man detained in Amsterdam on September 15 and a suspect detained in Jordan on September 29, based on reporting by Reuters and other outlets. The FBI said the Dutch detainee was one of the alleged leaders and that Dutch police acted under Dutch law with FBI support. ShinyHunters told The Hacker News that he had no association with the group.
The Jordanian suspect, identified by Reuters’ sources as Saif al-Din Khader, is cooperating with the FBI, Reuters reported. The agency has not said whether that cooperation led to the Pennsylvania arrest. CBS News also reported that other suspected co-conspirators remain at large.
Patch failure under review
The investigation has focused attention on the system through which the data was obtained. In the breach account involving the reported Oracle PeopleSoft breach, the reported target was Oracle PeopleSoft, while the FBI has not publicly named either the platform or the outside organization responsible for managing it.
Brett Leatherman, assistant director of the FBI Cyber Division, told Reuters on October 5 that the review had found a contractor failed to implement a security patch explicitly issued to secure the platform. The FBI removed the contractor. Two sources told Reuters that the software was PeopleSoft, Oracle’s human-resources product, and that Accenture was involved; Accenture said it was proud to support the FBI’s mission and did not answer Reuters’ questions about the contractor.
Reuters’ analysis of a sample shared by ShinyHunters found extensive personal information on FBI employees, sensitive job-role details, and psychiatric and medical information. CBS News reported that an internal FBI notice confirmed that employee information had been obtained.
Business implication
For organisations using externally managed systems, the case makes patch assurance a governance issue rather than a routine operational task: businesses should establish who owns each critical update, require evidence that it was deployed, and define escalation procedures when a supplier misses a security deadline.