


FortiMail flaw under attack enables unauthenticated file writes
CISA adds actively exploited FortiMail flaw to KEV catalog
The U.S. Cybersecurity and Infrastructure Security Agency has added CVE-2026-104286, a critical vulnerability in Fortinet FortiMail, to its Known Exploited Vulnerabilities catalog after reports of active exploitation. The issue has a CVSS score of 9.8 and can allow an unauthenticated attacker to write arbitrary files to the underlying system.
Fortinet said crafted HTTP or HTTPS requests can trigger the flaw. The advisory identifies a path-traversal weakness, tracked as CWE-22, together with improper neutralisation of NULL bytes or NULL characters, CWE-158. Fortinet credited Gwendal Guégniaud of its Product Security team with discovering and reporting the vulnerability.
Affected releases and available mitigations
The affected versions are FortiMail 8.0.0 through 8.0.1, FortiMail 7.6.0 through 7.6.6, FortiMail 7.4.0 through 7.4.8, and FortiMail 7.2.0 through 7.2.9. Fortinet advises upgrading 8.0 installations to 8.0.2 or later, 7.6 installations to 7.6.7 or later, and 7.4 installations to 7.4.9 or later when those fixes are available. Customers on 7.2 should move to the 7.4 branch or later.
Until fixes are available for affected branches, Fortinet recommends disabling IBE feature support with its documented CLI configuration and removing internet access to the FortiMail management interface. Where complete removal is not feasible, management access should be limited to trusted private networks.
Indicators supplied by Fortinet
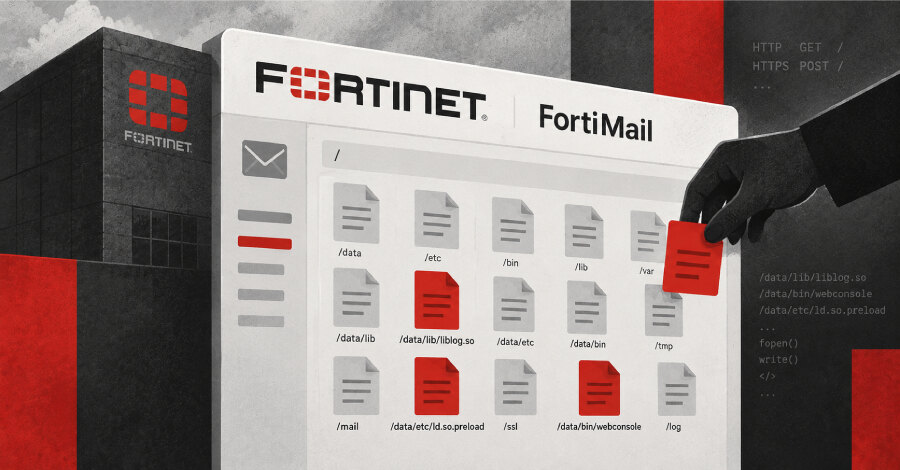
Fortinet published indicators that organisations can use during incident review. The listed IP addresses are 79.141.169[.]187 and 45.129.0[.]192. The company also identified added files including /data/lib/liblog.so, /data/bin/webconsole, /data/bin/mailservice, /data/etc/ld.so.preload, as well as modifications to /bin/smit, /data/etc/httpd.conf, and /data/migadmin.tar.gz.
Response priority for affected organisations
For Federal Civilian Executive Branch agencies, CISA recommended applying the patch or the available workarounds by October 4, 2026. The addition to KEV places the FortiMail issue among vulnerabilities that have been observed being used in attacks, rather than merely reported or theoretically exploitable.
Teams running FortiMail should establish which affected versions are deployed, check whether the management interface is internet-accessible, apply the relevant upgrade or interim mitigation, and examine systems for Fortinet’s published indicators. That sequence gives security and operations teams a concrete basis for prioritising an actively exploited exposure while permanent fixes are rolled out.