


Help TDS tied to Hotejka amid 20,000 Cloudflare Pages scam domains
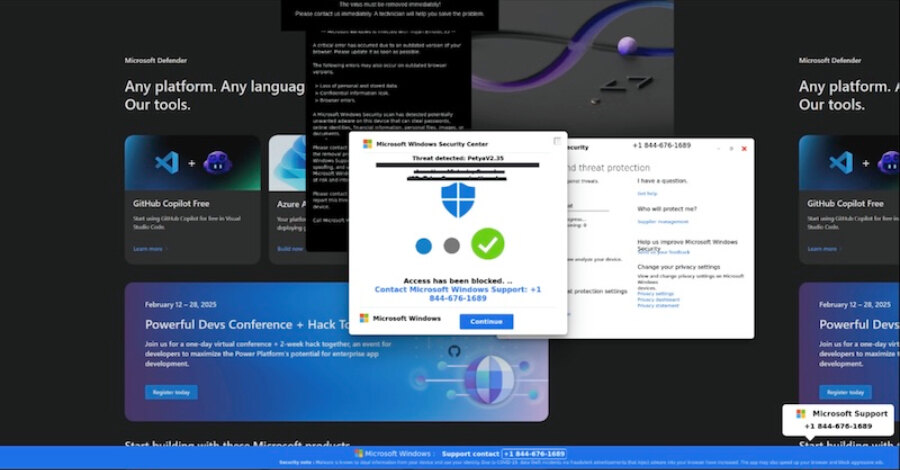
Infoblox has linked the long-running Help Traffic Distribution System (TDS) to Hotejka, a Russian-language affiliate programme believed to be a rebrand of ROI777. Since April 2026, the operation has used free Cloudflare Pages sites to run tech-support scams, creating roughly 300 disposable pages per day and exceeding 20,000 detected domains.
Help TDS has been active since at least 2017. Its affiliates direct visitors from compromised websites through specially crafted URLs, after which the TDS evaluates the visitor and selects a destination. The resulting campaigns include fake Microsoft Windows security alerts, browser-locking tactics and landing pages intended to pressure users into calling a purported support number.
Traffic routing behind the scam pages
A TDS acts as routing infrastructure between traffic sources and scam destinations. Infoblox said Help TDS uses browser fingerprinting and location data to decide what a visitor sees. It can filter traffic on criteria such as geographic location, device metadata, IP reputation and signs of headless browsing, then dynamically route users to scams, browser lockers or malware delivery pages.
The system is believed to run on Keitaro, an advertising performance tracking platform that has also been abused by other threat actors. Some users receive a sequence of Windows-themed prompts: an alleged update warning, a claim that Microsoft has disabled the machine, and instructions not to restart it because a “computer lock” supposedly blocks illegal activity.
The objective is to prompt a phone call. Infoblox said the call centres use social engineering to persuade victims to install free remote-desktop software, including UltraViewer, giving the operator control of the machine. Other traffic may be passed to an affiliate marketing platform for another assessment and resale, while some routes end at fake CAPTCHA pages designed to subscribe browsers to push-notification spam.
Hotejka, ROI777 and compromised WordPress sites
Infoblox assessed Hotejka and ROI777 as the same operation with high confidence, citing historical DNS records, continued use of affiliate advertising platforms and consistent command-and-control mechanisms. GoDaddy identified roi777[.]com as a historical command-and-control domain used between 2018 and 2020 to retrieve redirect destinations.
GoDaddy had also documented Help TDS activity in August 2025, including a malicious WordPress plugin called woocommerce_inputs. The plugin was used on thousands of websites to steal WordPress credentials and retrieve redirection URLs from command-and-control servers. Hotejka affiliates can inject that plugin or a custom HTML block into compromised sites.
The connection also reaches back to Operation Prowli, which Guardicore Labs, now part of Akamai, exposed in June 2018. That campaign compromised vulnerable servers to deploy r2r2 cryptocurrency-mining malware and exploited WordPress and other content-management-system sites for traffic monetisation fraud. Data leaked from ROI777 servers in March 2018 included Telegram identities and campaign details; the leak is believed to have contributed to a rebrand while the group operated Disposable TDS, a precursor to Help TDS.
Affiliate ecosystem expands the exposure
About 20 affiliates, including Balada Injector, Detour Dog and DollyWay, are reported to send traffic to Help TDS. These operations are known for heavily targeting WordPress sites and redirecting visitors to scams and malware. Historical redirect-chain tracking also found Help TDS handing traffic directly to VexTrio Viper, an operator whose affiliate programme supports scams, riskware, spyware, adware and pornographic content.
Hotejka posts on its Telegram channel advertised forced browser-extension installations and tech-support pages described as difficult to exit. In a July 17 post, the operator claimed that a small call centre in Germany would handle 50–100 calls per day. Infoblox also observed Hotejka seeking email-spam traffic and WordPress administrator-panel access on forums such as CrackingX, with prices starting at $100.
For businesses, the practical response is to protect WordPress administrator access, inspect sites for unfamiliar plugins and injected HTML, and investigate unexpected redirects promptly. Users should be instructed not to trust unsolicited full-screen security alerts or call their displayed numbers, because the apparent warning can be the first step toward remote access to the device.