


US agencies warn of cyber risks to connected refrigeration
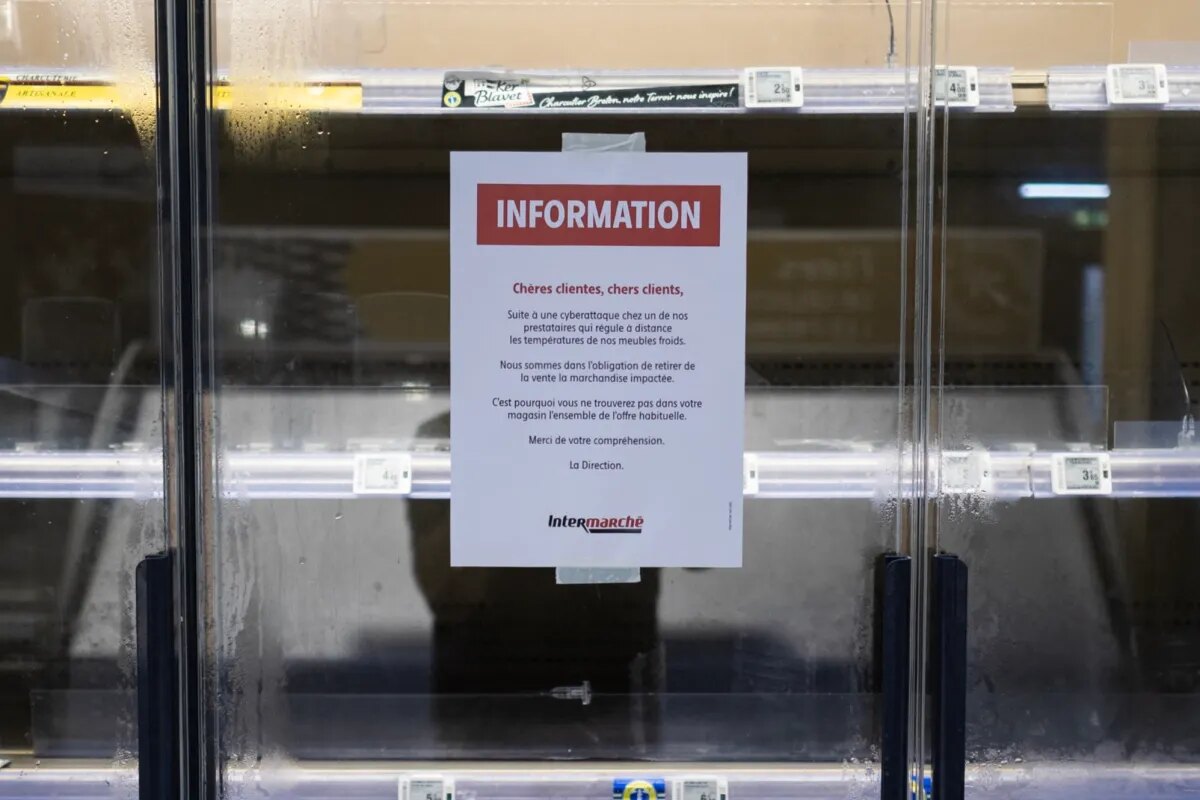
US cybersecurity agency CISA, the FBI, and the Departments of Agriculture, Health and Human Services, and Transportation have warned of an ongoing cyber threat to internet-connected industrial refrigeration and cold-chain monitoring systems. The alert covers equipment used by grocery stores, cold-storage facilities and sectors designated as critical infrastructure, including food, agriculture, transportation and medicine shipping.
The agencies said successful compromise could allow attackers to change a unit’s temperature. The potential physical consequences include fire hazards, inventory loss and changes to a system’s service life. A separate federal fact sheet warns that attackers may try to force units into continuous heating and defrost cycles, creating widespread inventory losses and equipment hazards.
Attacks have already disrupted refrigeration operations
The warning follows several waves of attacks on industrial refrigeration equipment in the United Kingdom and Europe. In two separate campaigns, attackers reportedly increased the temperature of freezers and chilling systems in at least a dozen countries, spoiling defrosted food and destroying produce.
Some affected systems were remote-controlled refrigeration units from Danish manufacturer Danfoss. The source reports that security updates had stopped for customers’ freezers. Attackers also targeted a blood bank in France, raising temperatures in refrigerated units holding donated blood supplies, but were stopped before the blood stores were compromised.
The US Department of Defense is also investigating a series of attacks against freezers operated by the military, Reuters reported. The United States has not attributed the incidents to a specific group or government. Security researchers have broadly linked the activity to Iran, and US officials reportedly suspect Iran is the likely culprit.
Federal guidance focuses on reducing remote exposure
CISA, the FBI and the participating departments urged affected organizations to remove remote-control systems from the internet, change and strengthen passwords, apply available patches and retire equipment that is no longer supported by its vendor.
“Every organization that depends on refrigeration and monitoring systems should assume it could be a target,” said CISA acting cybersecurity chief Chris Butera. The guidance makes the business implication direct: operators should identify exposed refrigeration and monitoring devices, restrict remote access, and set a replacement plan for unsupported systems before a digital intrusion can produce a physical disruption.