


Canonical patches critical LXD and MicroCloud client impersonation flaw
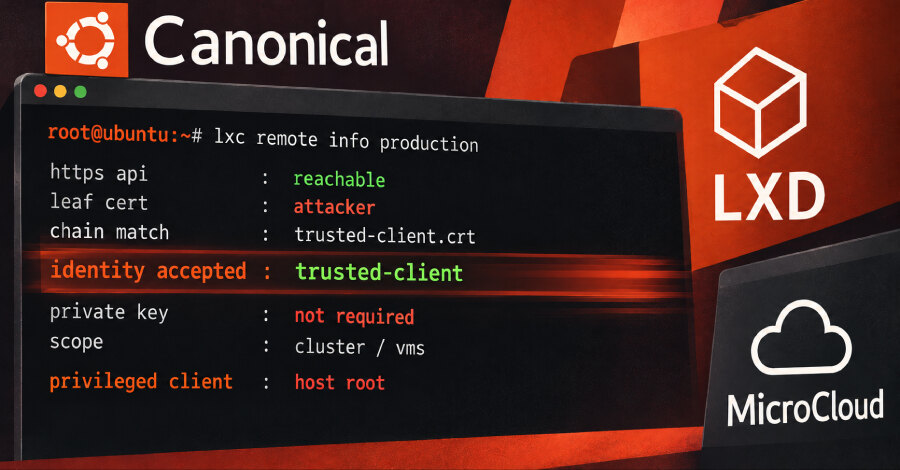
Canonical has released fixes for CVE-2026-112816, a critical vulnerability in LXD and MicroCloud that carries a maximum CVSS score of 10.0. The flaw can allow an attacker to authenticate to the products’ HTTPS APIs as a trusted client without possessing that client’s private key.
Successful impersonation can expose an LXD cluster and its virtual machines to the attacker under the permissions of the copied identity. Canonical said that impersonating a privileged account could result in root access to the host machine.
A certificate-chain validation failure
LXD and MicroCloud use mutual TLS for remote API access. Clients present certificates, and the server accepts identities whose certificates are held in its trust store. The vulnerable implementation compared every certificate supplied by a connecting client against that store.
However, a TLS connection demonstrates ownership of the private key only for the first, or leaf, certificate in the presented chain. Additional certificates are supplied by the connecting party. An attacker could therefore use their own certificate as the leaf and attach a trusted client’s public certificate elsewhere in the chain, causing the server to accept the connection as the trusted client.
The trusted certificate need not be secret. Exploitation requires network access to the HTTPS API and access to the public certificate of a client already trusted by the server. A standalone LXD installation does not expose its network API by default; it listens on a local socket unless an administrator enables the network listener through the core.https_address setting.
MicroCloud cluster exposure and affected releases
MicroCloud combines multiple LXD machines into a cluster. Canonical identified a cluster-specific risk: an attacker able to capture a member’s public certificate while that member joins the cluster can subsequently authenticate as that member.
The CVE record identifies affected LXD lines including 4.0.14, 5.0.10, 5.21.8 and 6.9 before their corresponding patched releases. Canonical lists fixed Snap versions as LXD 6.10.1 on the 6/stable channel, 5.21.9 on 5.21/stable, 5.0.11 on 5.0/stable and 4.0.15 on 4.0/stable. Fixed MicroCloud releases are 3.4.1 on 3/stable and 2.1.5 on 2/stable.
The issue was reported by Incus, the community fork of LXD, and Canonical confirmed that LXD was affected. Incus fixed the same flaw in version 7.6.0. Ubuntu archive packages of LXD are listed as not affected or not shipped, making the relevant remediations Snap releases.
Update and restrict the API listener
Canonical advised Snap users to run sudo snap refresh lxd and sudo snap refresh microcloud. Its advisory noted that the patched LXD point releases were moving from the candidate channel to stable, so administrators should check the installed version after refreshing rather than assume the update has arrived.
There is no configuration-level fix for LXD. Until updates are confirmed, limiting access to the HTTPS API reduces exposure because network reachability is required for the attack. CISA assessed the vulnerability on October 30 as not known to be exploited, and it is not on the Known Exploited Vulnerabilities catalog. The immediate business implication is to verify patched versions across LXD and MicroCloud deployments, restrict API access to authorised networks, and review privileged trusted-client identities.