


NGINX Releases Fixes for Five Configuration-Dependent Security Flaws
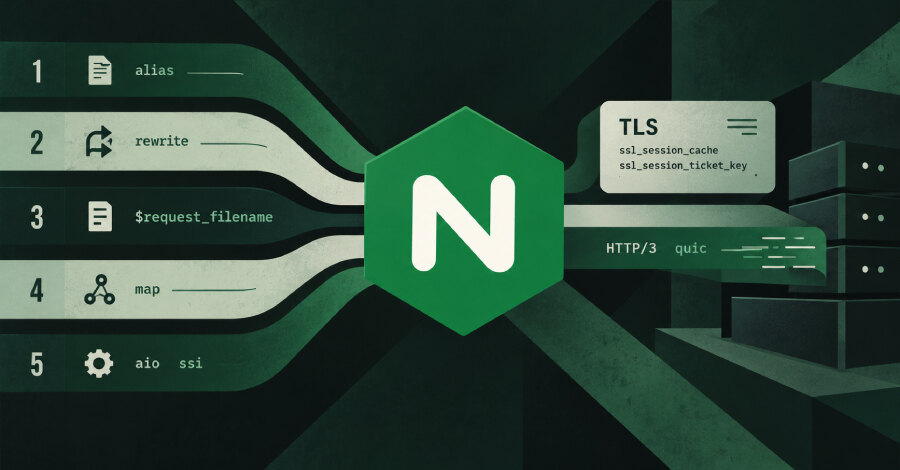
NGINX has released versions 1.30.6 and 1.31.7 to correct five security vulnerabilities affecting web-server configurations that use particular directives and features. Three flaws can crash a worker process and may permit code execution; F5 assigned each a CVSS v4.0 score of 9.2. The release also addresses a TLS session flaw that could bypass client-certificate verification and an HTTP/3 request-handling issue.
NGINX rates all five issues as medium severity. As of October 15, none was listed in CISA's Known Exploited Vulnerabilities catalog, and neither NGINX nor F5 had reported attacks. The fixes are available on the stable and mainline branches, while older branches remain affected unless a distributor has backported the patches.
Configuration determines exposure
The TLS vulnerability, CVE-2026-97629, affects deployments using ssl_session_cache shared without ssl_session_ticket_key, where NGINX automatically generates and rotates TLS session-ticket keys. Since version 1.23.2, workers maintained three key slots, but the rotation process copied only two. A ticket referring to the remaining slot could be processed with uninitialised key material, enabling a forged session in a non-deterministic manner beyond an attacker's control, F5 said.
The condition matters because NGINX documentation uses a shared session cache in its example configuration. Servers with ssl_session_tickets off are not affected. Where an immediate upgrade is not feasible, F5 recommends removing the shared-cache directive or supplying keys through ssl_session_ticket_key.
CVE-2026-95101 affects HTTP/3 deployments with proxy_request_buffering on, the default. If an unknown HTTP/3 frame is split across two reads, NGINX can treat remaining frame data as request-body data and send extra bytes to the backend beyond the client_max_body_size check. F5's temporary mitigation is to disable request buffering.
Three worker-process memory flaws
CVE-2026-15176 is a heap overflow involving a location that combines alias, a URI-changing rewrite and a read of $request_filename. The affected range runs from 0.1.29 through 1.31.6. F5 advises avoiding alias in that location and avoiding use of the variable until the software can be updated.
CVE-2026-93479 is another heap overflow, in regex-map captures referenced by root or log_format before the map output variable. It affects 1.30.0 through 1.30.5 and 1.31.2 through 1.31.6. The issue followed July changes to string handling; F5 recommends named captures used only within the matching block as a workaround.
The third memory issue, CVE-2026-97205, is a use-after-free condition in configurations with AIO enabled and SSI pages using include virtual commands. Pending asynchronous operations can wrap an unchecked 8-bit counter, freeing a request while operations still reference its memory. Turning off AIO or avoiding SSI pages removes the documented trigger.
Upgrade and verify the active configuration
Organizations should move to NGINX 1.30.6 on the stable branch or 1.31.7 on mainline, then verify whether distribution packages have incorporated the changes. NGINX Plus users and customers of F5 Ingress Controller, Gateway Fabric, Instance Manager and WAF should also check the relevant F5 advisories for affected builds.
A practical review starts with nginx -T: look for alias directives near rewrites, regex maps used by root or log formats, AIO combined with SSI, QUIC listeners, and shared TLS caches without an explicit ticket-key directive. This inventory lets teams prioritise upgrades and apply the stated configuration mitigations where maintenance windows delay patching.