


Decision Models Shift the Economics of AI SOC Alert Triage
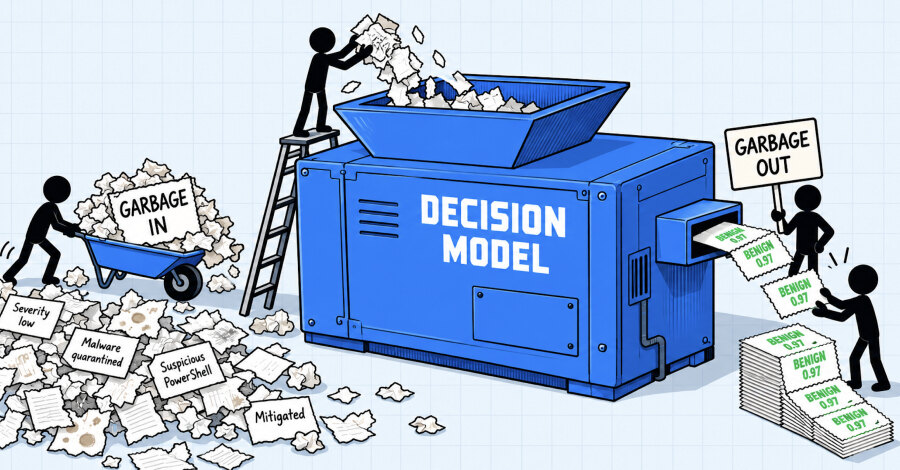
Decision-focused AI models are emerging as a new option for security operations centres: rather than generating prose, they return a typed choice, score or yes-or-no answer with an attached probability. TypeSafe AI released Jev on September 15, OpenAI opened a public beta of its Decisions API on October 6, and Cribl published cribl-decision as an open LoRA adapter that can run locally.
The attraction for AI SOC platforms is straightforward. A probability can be tied to an operational threshold: an alert judged benign above 0.97 might be closed automatically, one below 0.6 escalated, and the middle range sent to an analyst. TypeSafe AI lists Jev at $42 per billion input tokens and reports 70 to 500 millisecond responses. Using a few thousand tokens per alert, an organisation processing 450,000 alerts annually could face a model bill of roughly $100 in the example described.
Cheap decisions do not make weak inputs reliable
Structured outputs improve auditability because teams can log, replay and compare each verdict with the eventual outcome. They do not guarantee correctness. A model can comply with a defined schema while still reaching the wrong conclusion, and calibration only describes performance across inputs resembling those used to assess it.
That distinction is consequential in triage. The AI SOC Report 2026 cited 25 million alerts triaged during 2025. Of 82,000 alerts that triggered a live endpoint memory scan, about 2,600 machines had an active infection. Yet 51% of those infected systems had already been reported as mitigated by endpoint detection and response tooling. An alert labelled malware detected, threat quarantined and low severity may therefore appear safe while omitting the machine-level evidence needed for a sound decision.
Severity is also an incomplete filter. Nearly 1% of real incidents in the reported data originated in alerts at the lowest severity levels, equivalent to roughly 54 threats a year for an organisation receiving 450,000 alerts. Cribl’s model card notes that its model can be overconfident and is sensitive to the wording of prompts and candidates. Those limitations make input quality and local validation central to automation.
Evidence and organisational context remain the hard part
Useful investigation context goes beyond an alert title, a hash or a reputation score. Process trees, parent processes, full command lines, scripts, sandbox behaviour, network activity and live memory examination can establish what executed and whether malicious activity remains present. The article highlights Mimikatz, Meterpreter and Cobalt Strike as common memory-resident tools that file-based quarantine status may not reveal.
For identity events, organisations also need to know what is normal in their own environment. In the cited 2025 data, 74% of identity alerts were classified as likely benign; impossible-travel alerts were confirmed compromises only about 2% of the time, and VPN use accounted for around 30% of them. That context is specific to assets, users, workflows and detection rules, and it changes as the environment changes.
Build the feedback loop before expanding automation
The practical pattern is to collect forensic evidence before making a decision, use live context when prior case history is insufficient, and write investigation outcomes back into organisational knowledge. Every automated verdict should be linked to what later happened, allowing teams to test whether a stated 90% confidence level remains meaningful for their own alerts.
Decision models can make the final classification step fast, inexpensive and easier to audit. The business implication is to invest first in evidence collection, continuously refreshed organisational context and outcome measurement, then apply automation thresholds that match the reversibility and risk of each action.