


Binance describes attack chain behind $6.43 billion asset theft
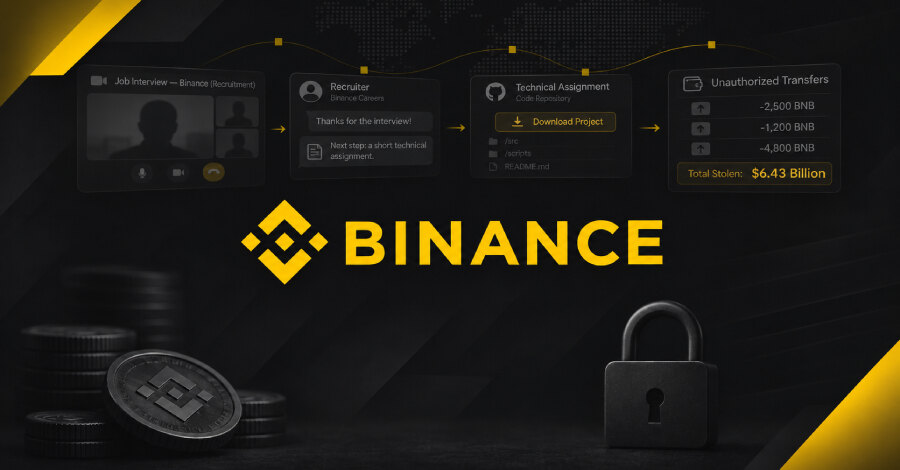
Binance has described a sophisticated, multi-stage intrusion that it says led to the theft of $6.43 billion in assets from the cryptocurrency exchange. The campaign targeted members of its Wallet DevOps and wallet software engineering teams, combining a trojanized Homebrew installer, recruitment-themed social engineering, compromised internal AI tooling and unauthorised access to a wallet signing service.
The company said the activity was not a single phishing incident. It unfolded from June through October 2026 and culminated on 29 October, when an attacker deployed a container and triggered a malicious script using credentials obtained during the compromise.
Developer tool search created the first opening
Binance traced the first stage to June, when Wallet DevOps Engineer A searched for a popular AI tool and downloaded a trojanized Homebrew installer. The installer was part of a supply-chain attack. Binance detected the incident and rotated related credentials, but said information about the engineer's role and colleagues working on wallet infrastructure was exposed.
That information was then useful to the adversary in preparing the next phase. The case illustrates how compromise of a developer environment can expose not only secrets or local access, but also organisational context that supports more credible targeting.
Fake interviews delivered malicious code
In September, the threat actor contacted Engineer B through a legitimate job-hunting platform while posing as a Project Director. A first-round video interview with an apparent HR representative included a social media account with personal photos and videos intended to establish credibility.
A purported second-round interview followed on a social chat application with someone claiming to be the chief executive of a non-existent company. Near its end, Engineer B was asked to download an “assignment” repository to a work computer. Binance said malicious code executed during setup and began unauthorised activity.
The malware used obfuscation and evasion methods, including replacing a legitimate development-tool component with a poisoned version. It executed commands, communicated with an attacker-controlled external server and removed forensic artefacts connected to the compromise.
AI tool and deployment access enabled the final stage
On 20 October, the attacker used Engineer B's compromised machine and abused an internal AI tool to gain control of Engineer A and Wallet Software Engineer C. The attacker found a container deployment permission token on Engineer A's computer, Binance said.
Between 17:15 and 19:56 on 29 October, the attacker accessed Engineer C's computer, used credentials stolen from Engineer A, deployed a container and launched the malicious script. The intrusion then used unauthorised access to an internal wallet signing service to initiate transactions outside the normal withdrawal process.
Systems rebuilt after the incident
Binance said it reconstructed the affected wallet system in a new environment, rebuilt its internal AI tool and access controls, replaced affected devices, and decommissioned relevant credentials and tokens. It also completed enhanced scans across employee devices, strengthened wallet-service risk controls and expanded AI-based behavioural anomaly detection.
The exchange said it is working with law enforcement, blockchain intelligence firms and industry partners to trace and freeze affected assets. It also reported having foiled 57 suspected North Korea-linked cyber threat cases since the start of the year, citing recurring tactics such as fraudulent interviews, malicious developer tools, compromised packages, browser extensions and fake video-conferencing applications.
For organisations, the practical implication is to apply consistent scrutiny to software installation, code-repository setup, recruitment interactions and AI-tool permissions, because an attack can move across all of those environments before reaching a high-value service.