


ChainScript RAT uses Polygon for rotating command-and-control
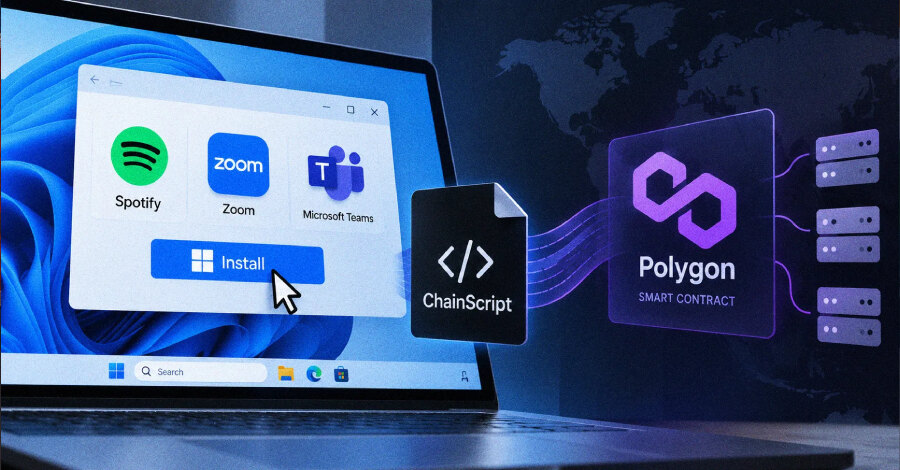
Blackpoint Adversary Pursuit Group has identified ChainScript, a previously undocumented remote access trojan delivered through ClickFix-style lures. The malware uses a Polygon smart contract to discover its live WebSocket command-and-control infrastructure, enabling operators to redirect infected hosts while keeping the same implant and reconnect workflow.
Researchers observed ChainScript under the build names ComponentTask33, UpdateDigital, HostShared and OrchidViolet66. It has also presented itself as Spotify, Zoom Workplace and Microsoft Teams software. The RAT offers interactive CMD and PowerShell access, file operations, screenshot capture, payload deployment, cryptocurrency wallet enumeration and remote JavaScript execution.
Installer chain deploys a Node.js-based agent
The observed attack begins with a ClickFix lure that leads to a malicious Windows installer executed with msiexec.exe. One sample, named ComponentTask33-4d14e6ac.msi, was disguised as Spotify. It deploys the Node.js runtime and starts the ChainScript JavaScript agent through hidden PowerShell and VBScript stages.
The PowerShell stage writes the runtime, agent source, configuration and auxiliary binaries into Microsoft-looking paths under %LOCALAPPDATA%. A VBScript acts as the main launcher. Once running, the agent establishes user-level persistence through a scheduled task, with a Registry Run key as a fallback.
After execution, ChainScript connects to its command server over WebSockets and retrieves further tasking, giving the operator direct control of the compromised device. Its command set includes the ability to update itself and remove persistence, features that can complicate incident response and artefact collection.
Blockchain discovery complicates infrastructure tracking
Blackpoint describes the C2 discovery model as EtherHiding-style: the implant consults a Polygon smart contract to identify active backend infrastructure. By separating discovery from the malware binary, the operator can rotate servers without changing the agent installed on endpoints.
This approach makes indicator-based blocking less durable when defenders focus only on a single host, domain or network address. The pattern aligns with ClickFix attack chains and detection patterns on ClickFix attack chains and shows why detection needs to cover user execution, installer behaviour, script stages and outbound WebSocket activity.
The disclosure also coincides with PasteSwitch, a ClickFix operation in which a compromised verified HBO Max Reddit account served 108 malicious advertisements over 48 hours in mid-September 2026. The campaign delivered MacSync, Atomic macOS Stealer and fake cryptocurrency wallet applications to macOS users, while its Windows branch distributed Amatera Stealer and cryptocurrency clippers including AnimateClipper and ZigClipper.
Trusted presentation remains part of the attack path
Other observed ClickFix activity used a fake Codex download journey in search results and bogus Google Sites pages to persuade macOS users to paste a malicious command into Terminal. Cato Networks said the command retrieves a shell-script loader, decodes an embedded blob with eval, then records execution and downloads a final Mach-O payload.
Microsoft separately reported a macOS ClickFix campaign distributing MacSync and Atomic Stealer through at least 250 look-alike domains. The campaign evolved to use server-side browser fingerprinting to show the lure mainly to environments that appeared to be genuine macOS browsers, reducing exposure to crawlers, sandboxes and some automated analysis systems.
For businesses, the practical implication is to treat unexpected installer prompts and instructions to paste commands as high-risk events, even when they arrive through familiar brands or verified accounts. Endpoint visibility across msiexec, PowerShell, VBScript, scheduled tasks, Run keys and unusual WebSocket connections can help teams investigate the full execution chain rather than a single infrastructure indicator.