


French supermarket refrigeration disrupted through Danfoss controllers
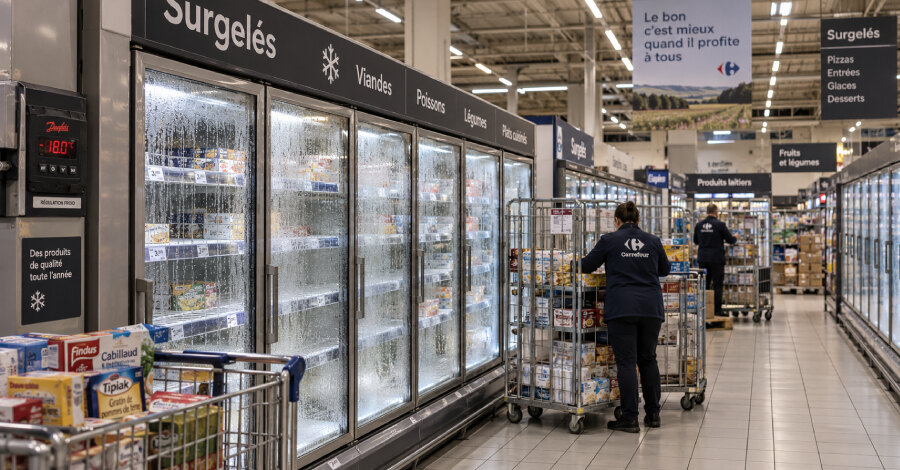
Attackers remotely disrupted refrigeration systems at hundreds of French supermarkets on the night of October 11, affecting Danfoss controllers used to manage store fridges and freezers. Les Mousquetaires, owner of Intermarché and Netto, said systems were switched into defrost mode and heated to as much as 50°C.
CERT-FR, the French government’s computer emergency response team, said on October 12 that it knew of numerous compromises involving the Danfoss AK-SM and AK-SC controller series. The alert instructed operators to disconnect the controllers or filter access to them. CERT-FR is part of France’s national cybersecurity agency, ANSSI.
Retailers report food losses and store disruption
Retail chains reported different numbers of affected sites. Les Mousquetaires said at least 300 Intermarché and Netto stores were reached in figures cited by AFP, while Reuters reported about 150 stores. Coopérative U reported 80 affected locations, Carrefour 80 supermarkets and Monoprix about 30; E.Leclerc said several stores were affected.
Being reached by the attack did not necessarily mean a store lost its stock. Coopérative U chief executive Dominique Schelcher said the cold chain held in most affected stores and that only a minority could not react quickly enough. Intermarché said affected stores had to discard all products concerned. Thierry Cotillard, who heads Les Mousquetaires, expected losses in the tens of millions of euros across France, Reuters reported.
The Paris prosecutor’s office has opened an inquiry led by its cybercrime section and assigned to the anti-cybercrime office, OFAC. The inquiry is intended to count victims and establish the link between the attack and reported damage, including spoiled food and equipment that began to catch fire.
Older controllers lack security updates
Danfoss said most impacted systems were older products that no longer receive software or security updates: the AK-SM 800, declared end-of-life in May 2021, and the AK-SC 355, phased out in 2016. Some current AK-SM 800A controllers were also affected, and Danfoss said those devices were running outdated firmware.
For the AK-SM 800A, Danfoss listed package 5.3.x as the latest software package on October 13. Its documentation says systems on version 3.x must first move to 4.x, while controllers running 5.3.x cannot be downgraded. Starting with version 4.0, Strict Session Control is enabled by default and requires HTTPS.
Access controls are the immediate priority
CERT-FR did not identify a vulnerability, firmware version or confirmed initial-access route. It warned that exposing a management interface to the internet is contrary to good practice. Where remote administration is unavoidable, it recommends allowing only trusted IP addresses as an initial temporary safeguard.
For potentially compromised controllers, CERT-FR advises limiting network access to service providers, performing a factory reset, applying available fixes, changing passwords and other device secrets, reviewing accounts, and rebuilding the configuration. Owners of the unsupported AK-SM 800 and AK-SC 355 cannot obtain new fixes, so replacement is the path Danfoss recommends.
The practical implication for retailers and refrigeration contractors is to identify every internet-reachable controller, tightly restrict remote maintenance paths, update supported devices, and schedule the retirement of unsupported systems before a disruption can turn operational technology exposure into food loss and equipment damage.