


Danfoss AK-SM800A flaws expose refrigeration controllers to takeover
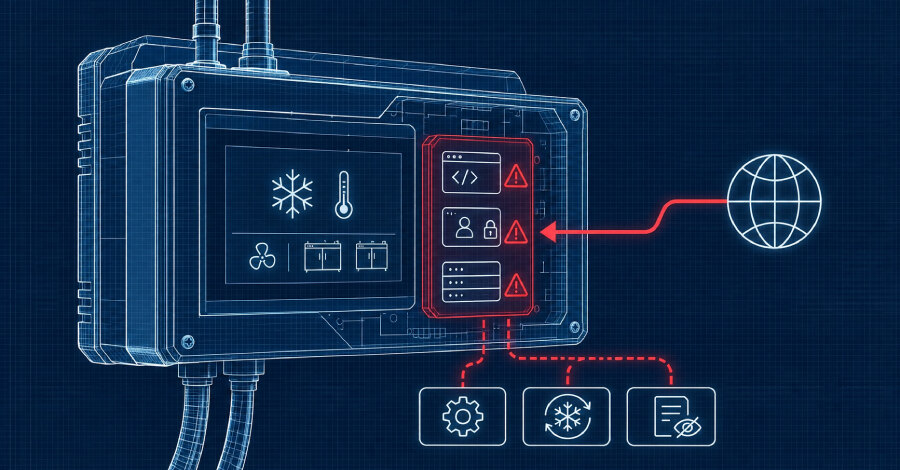
Six unpatched vulnerabilities in Danfoss AK-SM800A refrigeration controllers could allow a remote attacker to take over a controller without logging in. Dutch security consultancy Midnight Blue reported that the flaws affect firmware through version 5.4.0, Danfoss’s newest listed software package for the product, and that no patch or remediation date has been published.
The AK-SM800A manages refrigeration equipment such as shop fridges and freezers and can be administered remotely by maintenance firms. Government cybersecurity agencies in Belgium, Ireland and Germany have advised operators to remove the controllers’ management interfaces from the public internet, including exposure provided through 4G or 5G modems.
Strict mode is not a sufficient boundary
Midnight Blue examined firmware version 5.3.2 and said that every version up to and including that release was affected. The researchers also stated that version 5.4.0 does not fix the six flaws. Danfoss’s November update guide describes upgrade steps and a stricter password requirement, but does not mention fixes for these issues.
Five vulnerabilities are located in web request handlers that accept requests without authentication in a program running as root. On older version 3.3.0 firmware, the researchers used one of the issues to execute code as root, and they found the same bugs in version 5.3.2.
Strict mode reduces the web attack surface available to unauthenticated users by requiring encrypted connections and session tokens. However, the sixth flaw is in the separate gateway that enforces that protection. In an emulated version 5.3.2 system with Strict mode enabled, Midnight Blue found that the issue could crash the gateway. The researchers said further work could turn that crash into code execution, while noting the gateway lacks protections such as stack canaries.
Potential operational consequences
Root-level code execution could enable an intruder to alter controller settings, initiate defrost cycles and hide activity from logs. The researchers also found no secure boot mechanism, meaning malicious code could potentially survive both a factory reset and a firmware update. An attacker could also render a controller unusable until it is replaced.
The BSI said the AK-SM800A had been involved in earlier incidents in which refrigeration units in several countries were tampered with. It has no information that the six newly reported flaws were exploited, and neither the researchers nor other agencies linked them to those incidents. Attacks beginning in France on October 11 and then spreading across Europe reportedly caused unwanted defrost cycles and stock losses.
Germany’s BSI initially said version 5.4.0 was unaffected, then corrected its statement the same day to say it could not currently rule out that the release is affected. No CVE identifiers have been assigned, and Midnight Blue is withholding technical details while coordinating disclosure with Danfoss.
Actions for operators
Belgian and Irish guidance says updating firmware, changing default passwords and enabling Strict mode are not enough where a management interface remains internet-accessible. Danfoss’s own update guidance also says the AK-SM800A should not be directly reachable from the public internet, including when Strict mode is enabled.
- Identify every controller exposed to the internet, including through mobile modems, and remove that exposure.
- Provide remote maintenance through a secure VPN or a protected internal network; limiting firewall access to service-company addresses is only a short-term measure.
- Review temperature setpoints, defrost schedules, alarms, accounts and remote-access settings for unauthorized changes.
- If compromise is suspected, change all credentials and verify that connected refrigeration equipment operates correctly.
Before stopping data flows to a refrigeration service company, operators should check contractual and insurance obligations and arrange protected remote access so monitoring continues. The immediate business implication is to treat public exposure of these controllers as an operational risk requiring network isolation and configuration checks now, rather than waiting for a firmware fix.