


Four inputs for prioritising exposures beyond CVSS severity
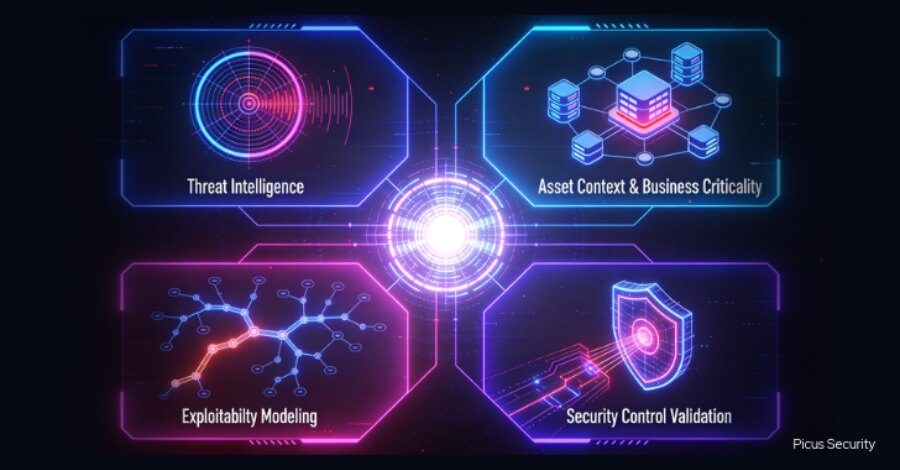
Picus Security has outlined a four-part approach to exposure prioritisation that moves vulnerability management beyond CVSS severity scores. The framework combines threat intelligence, asset context and business criticality, exploitability modelling, and security-control validation to determine which findings merit urgent action.
The company cites Gartner’s view that fewer than 10% of vulnerabilities are exploited, even though organisations commonly treat most of them as urgent. Gartner also argues that CVSS alone does not predict real exploitation or business impact, and predicts that by 2028 organisations using all four inputs will reduce breach likelihood by at least 70% compared with peers relying chiefly on CVSS-based prioritisation.
From severity labels to evidence-based decisions
Severity-based triage was designed for a less dynamic environment. Enterprises now face large volumes of vulnerabilities spanning cloud services, SaaS, identity systems and supply chains. Picus argues that compliance requirements, legacy metrics and fragmented ownership can keep teams focused on what is readily auditable rather than what poses the most meaningful risk.
In the proposed model, threat intelligence supplies the adversary perspective by identifying exposures attackers are exploiting. Asset context determines whether the affected system supports critical functions, processes regulated data or offers a route towards more valuable systems. This information may already exist in scanners, CMDBs, cloud-security platforms and identity systems, but it must be unified and kept current.
What the four signals contribute
Exploitability models, including EPSS, estimate the likelihood of exploitation from factors such as exploit complexity, component prevalence and the period between disclosure and exploitation. Picus stresses that such models are a filter, not a final verdict: they describe statistical likelihood in general, whereas testing is needed to establish what is exploitable in a particular environment.
Security-control validation provides that environmental evidence. It assesses exposures against deployed segmentation, endpoint protection, detection coverage and identity controls. A highly rated flaw may be unreachable behind existing defences, while a lower-rated issue on a poorly monitored asset may represent the more serious exposure.
Picus describes three validation methods on its platform: Breach and Attack Simulation, Autonomous Penetration Testing and Exposure Validation. The latter maps a CVE to the attacker techniques required and tests those steps against existing controls without firing an exploit, which the company says can support evidence-based decisions even for assets that cannot be tested live.
One workflow rather than four disconnected inputs
The operational challenge is that threat intelligence, asset data, exploit scores and control assessments often sit with separate teams or tools. Picus groups its process into a continuous Discover, Validate, Prioritize and Mobilize loop, with remediation initiated after priorities are checked in context.
For security leaders, the practical implication is to measure outcomes such as the time from threat publication to testing and remediation, the quality of control coverage, and the backlog of exposures demonstrated to be exploitable. Combining those measures can help teams decide whether to fix, mitigate or accept a finding using evidence rather than severity alone.