


US Offers Reward for Zhang Yu in HAFNIUM Exchange Case
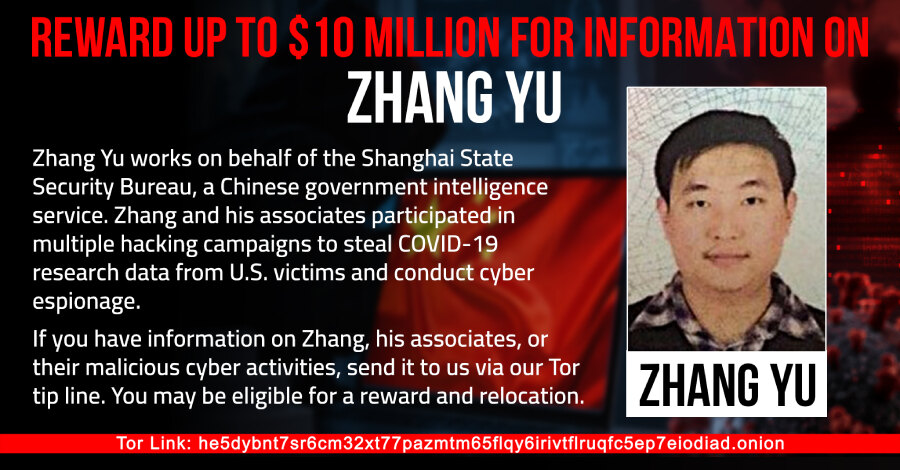
The U.S. State Department is offering a reward of up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged in the United States over alleged involvement in the 2021 Microsoft Exchange Server intrusions known as HAFNIUM. Zhang remains at large, while the charges have not been tested in court.
The notice, reported by NTD and issued through the State Department's Rewards for Justice programme, concerns alleged malicious cyber activity against U.S. critical infrastructure. Rewards for Justice is the department's national-security rewards programme and says it has paid more than $250 million to over 125 people since 1984.
A nine-count federal case
Zhang and Xu Zewei are named together in a nine-count indictment in federal court in Houston. The indictment is dated November 2023 and was unsealed in July 2025. The Justice Department has sought public assistance in locating Zhang since then.
Xu was arrested in Milan in July 2025 at the request of the United States and extradited by Italy in April 2026. At that time, FBI Cyber Division assistant director Brett Leatherman said Xu was among contractors the Chinese government uses to obscure its role in cyber operations.
U.S. authorities identify Zhang as a director of Shanghai Firetech Information Science and Technology. The indictment alleges he worked on assignments from the Shanghai State Security Bureau, supervised hacking by Firetech personnel and coordinated activity with Xu. The bureau is part of China’s Ministry of State Security.
Xu allegedly worked for Shanghai Powerock Network. The Justice Department describes Powerock as one of the companies it says enabled hacking for the Chinese government, using private firms and contractors to conceal state involvement.
Two alleged intrusion campaigns
The indictment describes activity from February 2020 to June 2021. The first alleged campaign, in early 2020, targeted U.S. universities and scientists involved in COVID-19 vaccine, treatment and testing work. The second allegedly exploited Microsoft Exchange Server vulnerabilities from late 2020 in the campaign later labelled HAFNIUM.
On or about January 30, 2021, Xu allegedly told Zhang that he had compromised the network of a Texas university. The listed alleged victims include two Texas universities and an international law firm with an office in Washington, D.C.
Microsoft disclosed the Exchange attacks on March 2, 2021 and released patches for four zero-day vulnerabilities, including ProxyLogon. It assessed HAFNIUM as a state-sponsored group operating from China; Microsoft now tracks the group as Silk Typhoon. Other threat groups began exploiting the same flaws within days.
Why the case still matters
The FBI says the wider HAFNIUM campaign compromised more than 12,700 U.S. organisations. In July 2021, the United States and partner governments attributed the campaign to actors linked to the Ministry of State Security. The names Zhang Yu and Xu Zewei arise from the later U.S. indictment.
For businesses, the case reinforces the operational importance of quickly patching internet-facing collaboration infrastructure, preserving evidence during suspected compromise and maintaining an incident-response plan for widely exploited zero-day vulnerabilities.