


Hijacked HBO Max Reddit account used in ClickFix malware campaign
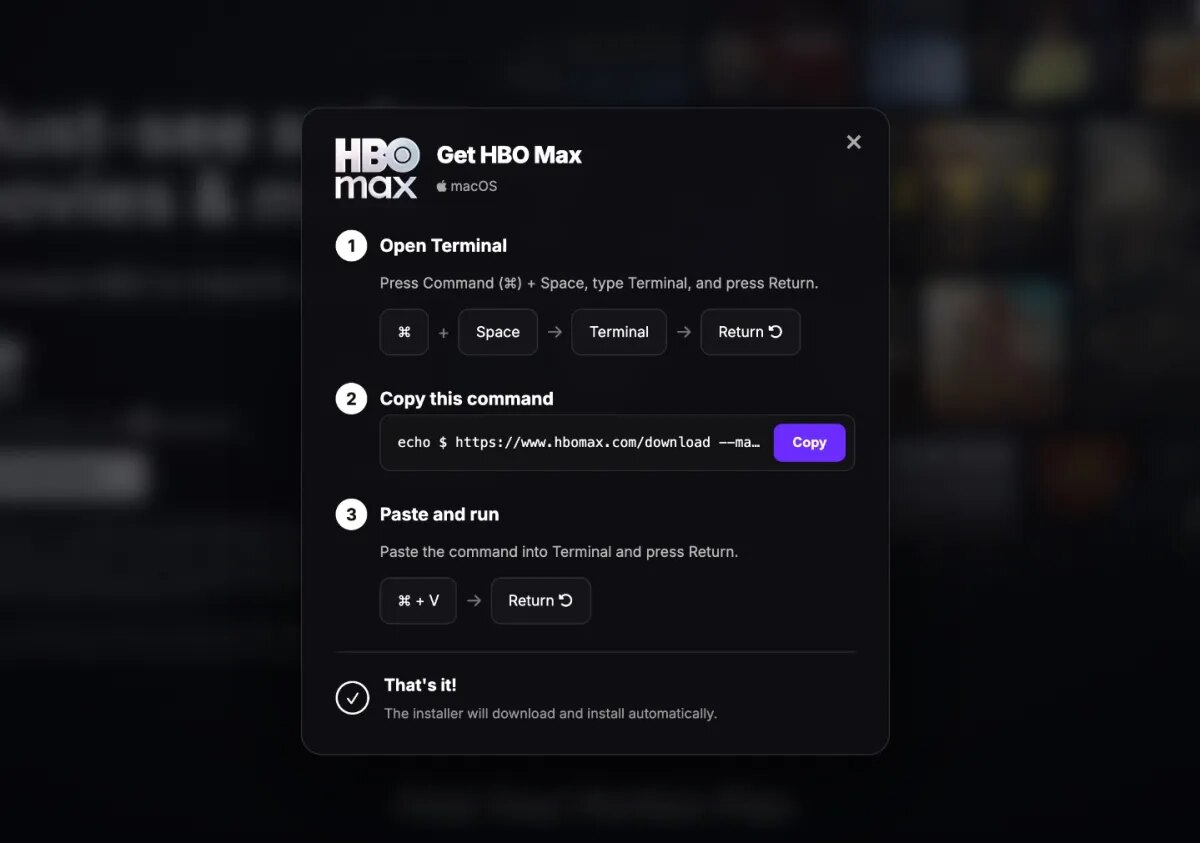
Security researchers have identified a ClickFix campaign in which attackers reportedly compromised HBO Max’s official Reddit account and used it to publish hundreds of fraudulent adverts. The posts linked to a page designed to resemble HBO Max but carrying a lure aimed at Mac and Windows users.
Hudson Rock and a discussion in Reddit’s cybersecurity community described the activity. The campaign’s scale is unclear: it is not known how many people opened the adverts or how many devices were compromised. Warner Bros. Discovery, HBO’s owner, and Reddit did not respond to requests for comment.
How the ClickFix lure works
ClickFix pages present what appears to be a CAPTCHA or anti-bot checkbox. After a visitor clicks it, the site displays instructions for a supposed verification step: copy a supplied text string and paste it into a local command interface.
On Windows, the instructions can direct a user to Command Prompt or PowerShell; on macOS, they use Terminal. Pressing Return executes the supplied command and can immediately install information-stealing malware. The malware may steal passwords, access to already logged-in accounts and cryptocurrency wallets.
The social engineering approach is particularly dangerous because the user runs the command directly in an operating-system terminal. That interaction can help such attacks evade antivirus and other defensive tools. The Mac-focused risk has also been documented in ClickFix macOS stealer campaign targeting cryptocurrency assets, where a stealer campaign targeted cryptocurrency assets through a similar user-executed mechanism.
Controls for managed endpoints
Command-line use is routine for many developers, but it is less common for typical users to work in Command Prompt, PowerShell or Terminal. That difference gives organisations a clear point for reducing exposure without treating every endpoint identically.
Security researcher Kevin Beaumont notes that organisations operating fleets of Windows computers can block access to these features across a domain. For macOS users, Ars Technica highlighted BlockBlock as a tool that can defend against attacks attempting to trick Apple users into executing malicious actions.
Business implication
Businesses should review which employee roles genuinely need terminal access, apply appropriate restrictions to managed Windows devices, and train staff to treat any CAPTCHA that requests copied commands as suspicious. A familiar brand, a hijacked social account and a realistic advert do not make an instruction to run a command safe.