


Pentagon personnel breach exposes records of about 3.1 million people
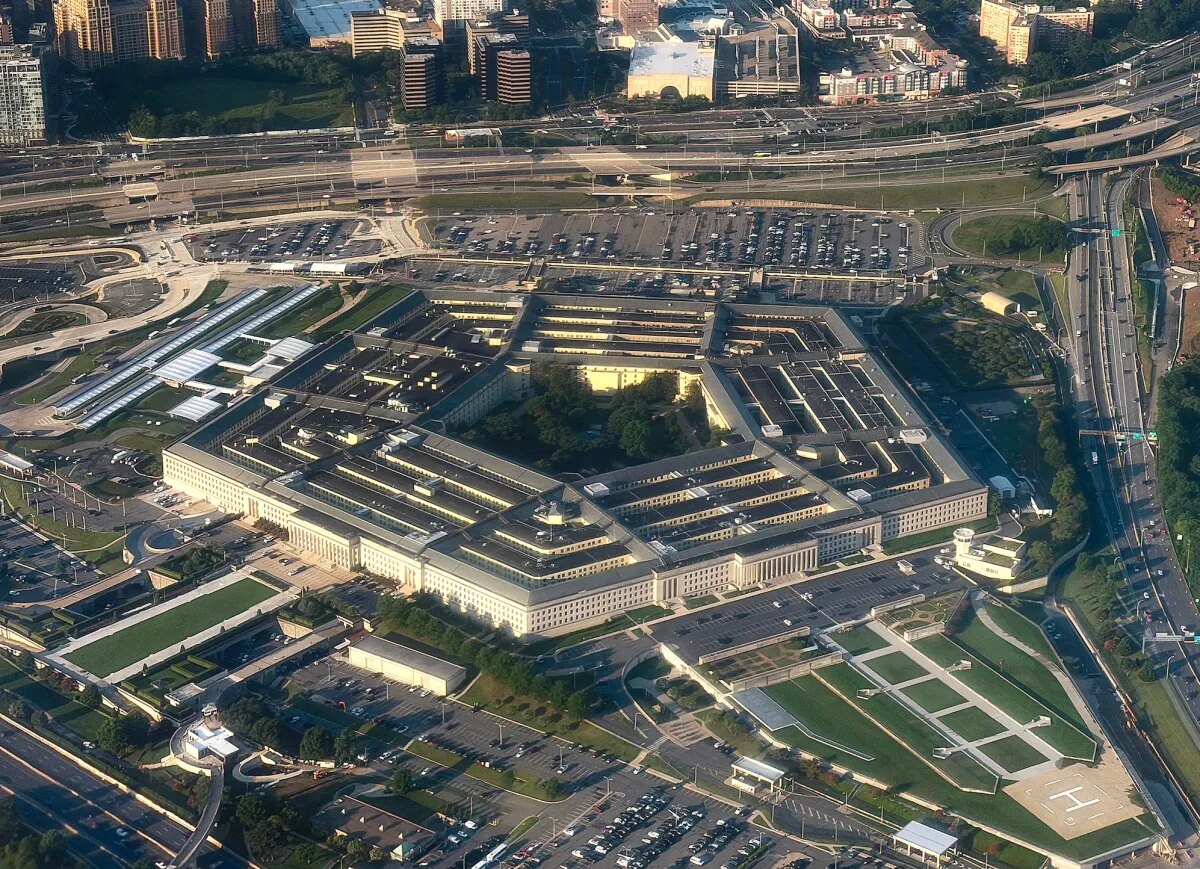
The U.S. Department of Defense is notifying current and former military service members and staff after a breach of Pentagon personnel records exposed data on about 2.8 million living people and close to 300,000 deceased individuals. The incident affected the Defense Manpower Data Center, or DMDC, a Department of Defense records-keeping unit.
A breach notification shared online states that several unauthorized users exploited a vulnerability in an unspecified file-sharing system over several months, from October 2025 until mid-July 2026. The notification did not identify the system, explain how the vulnerability was exploited, or name the attackers.
Unencrypted personnel information exposed
The stolen information included names, Social Security numbers, dates of birth, sex, race and other details of military service. The notification says the personnel records were unencrypted, increasing the sensitivity of the incident because the exposed fields can be used to identify individuals and assemble detailed profiles.
The scale is notable in relation to the armed forces. The U.S. military had 1.3 million active service members as of March, while the notification population also includes former personnel, staff and deceased individuals.
DMDC’s role extends beyond record keeping
DMDC holds more than 60 million records for U.S. military and civilian staff and their family members. Those records help establish eligibility for benefits and entitlements, including healthcare and retirement.
The organization also describes itself as the military’s leading identity-management provider. It links service members, employees and contractors to credentials such as smart cards and passwords used to access Pentagon computer systems, buildings and bases. That function makes the protection of its underlying identity data a critical operational concern, even though the reported breach concerns personnel records.
The Department of Defense said it had no indication that the information had been misused, but did not explain how it reached that assessment. No attribution has been announced, and the identities of the people behind the intrusion are unknown.
Federal personnel data remains a high-value target
The incident follows other recent thefts involving federal workers’ information, including a breach at the FBI reported in September. It also recalls the 2015 compromise of the Office of Personnel Management, which exposed private records of more than 22 million U.S. government employees, many with security clearances.
For organizations managing workforce identity data, the case is a practical reminder to identify unencrypted repositories, rapidly remediate file-sharing weaknesses, and closely monitor access to systems that combine personal records with credential and entitlement functions.