


Volt Typhoon Linked to Silent Train Zero-Day Operations
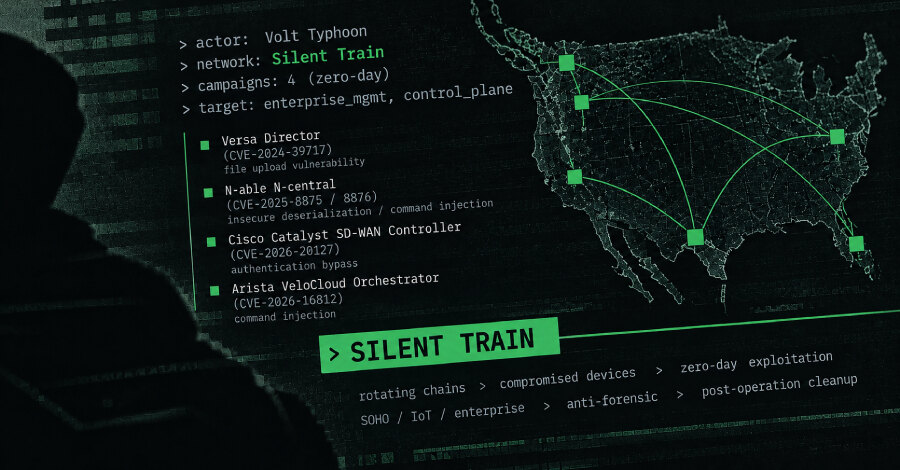
Lumen Technologies' Black Lotus Labs has linked the China-nexus espionage group Volt Typhoon to Silent Train, a covert access network used in four confirmed zero-day exploitation campaigns. The activity targeted enterprise management and control-plane technologies, including Versa Director, N-able N-central, Cisco Catalyst SD-WAN Controller and Arista VeloCloud Orchestrator.
Black Lotus Labs said Silent Train was first identified in late 2023 and was built from rotating chains of compromised SOHO, IoT and enterprise devices. Its stated role was to support vulnerability exploitation, credential access, data exfiltration and continued access to victim environments while making detection and attribution more difficult.
Four confirmed zero-day campaigns
The four campaigns include exploitation of the Versa Director file-upload flaw CVE-2024-39717. Volt Typhoon had previously used that vulnerability to deploy the VersaMem web shell, which was designed to harvest credentials and enable access to downstream customers.
The other confirmed flaws were CVE-2025-8875 and CVE-2025-8876 in N-able N-central, described as insecure deserialization and command-injection vulnerabilities; CVE-2026-20127, an authentication bypass in Cisco Catalyst SD-WAN Controller; and CVE-2026-16812, an operating-system command injection issue in Arista VeloCloud Orchestrator.
Black Lotus Labs also said Volt Typhoon is suspected of exploiting a likely zero-day in Quest KACE before it was patched in October 2025. That campaign is estimated to have affected more than 30 victims. The broader Silent Train activity identified hundreds of victims among telecommunications providers, government bodies, defense contractors, satellite and mission-critical communications services, universities, IT firms and critical-infrastructure operators.
A short-lived, layered relay network
Silent Train uses a layered, multi-hop design. Sessions begin from virtual private servers outside the United States, traverse compromised non-U.S. SOHO and IoT devices, and then use compromised U.S.-based devices as exit nodes before reaching domestic victims. This structure can obscure the traffic's point of origin and help evade geofencing and IP-reputation blocklists.
At least 27 device classes were exploited and enrolled, spanning products from TP-Link, Intelbras, Ruckus Wireless, SATO, NETGEAR, Zyxel and Cambium as well as enterprise platforms from Fortinet, Cisco, PRTG, Mirth Connect and CyberPanel. Operators exploited exposed web interfaces, installed only what was required for chained SSH access, and removed temporary SSH services, keys, configuration files and other artifacts after use.
Sessions lasted about four hours on average, with some surviving only minutes. By early 2025, Black Lotus Labs believes the network had developed into a hybrid model in which enterprise-grade devices were retained for one to three months. Later variants used reverse tunnels with open-source proxies Chisel and FRP.
Why centralized platforms are a priority
The reported targeting concentrated on endpoint-management platforms, network-management systems, SD-WAN orchestrators and control-plane technologies. Black Lotus Labs described these systems as valuable because they can provide visibility, control and access across large enterprise environments, including downstream customers and sensitive networks.
Hawaii, California and Texas emerged as U.S. focus areas for Silent Train operations. Black Lotus Labs linked that pattern to the presence of military installations, telecommunications infrastructure, defense contractors, satellite communications providers and critical logistics networks in those states.
For businesses, the immediate implication is to treat exposed management interfaces and orchestration platforms as high-priority attack surfaces: apply vendor fixes promptly, restrict external access, review authentication and logging, and investigate short-lived SSH or proxy activity that may disappear before routine monitoring detects it.