


WordPress patches Click2Shell forced theme installation flaw
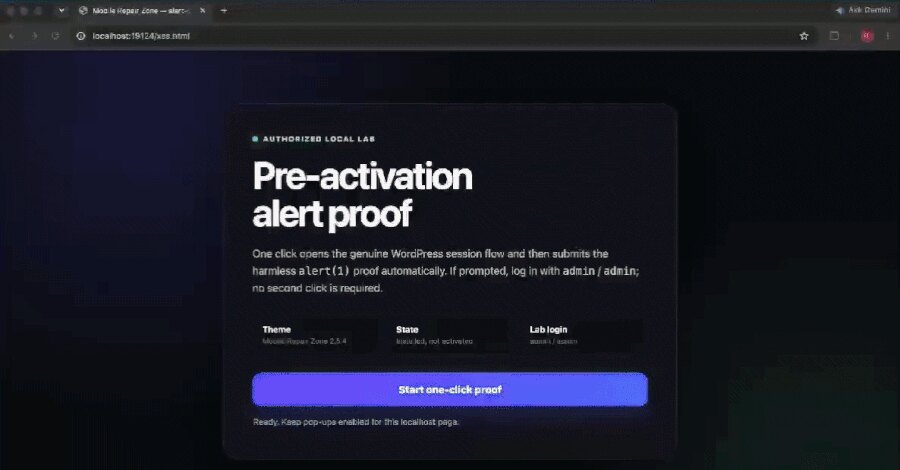
WordPress has released version 7.1.1 to fix Click2Shell, a core vulnerability that can cause a logged-in administrator’s browser to install a theme from the official WordPress.org directory after the administrator opens a specially crafted link. Security firm pwn.ai, which reported the issue, rated the forced-install bug as high severity with a CVSS score of 7.1.
The researchers also demonstrated a separate attack chain that reached server-side code execution when the forced installation was followed by a vulnerability in the selected theme. They rated that full chain 9.6, although WordPress has not issued its own severity score and no CVE identifier has yet been assigned.
How the forced installation works
The issue stems from two WordPress components interpreting the same URL differently. The WordPress.org directory treats a value in the link as an ordinary theme name and returns a legitimate theme. The administrator’s browser, however, reuses the original value, including attacker-supplied punctuation, in code that identifies an item on the page.
That crafted text can redirect the page logic to the Install button and cause WordPress’s own script to activate it. Since the administrator is already authenticated, the existing session provides both the required permission and the security token. The attacker does not need to supply either credential.
The installed theme remains inactive, so the site’s appearance does not change. pwn.ai stressed that the core flaw alone cannot accept an arbitrary theme ZIP; it installs a real theme chosen from the WordPress.org directory. WordPress described the issue as one in which specially crafted URLs can automatically install and preview an inactive theme.
Why a separate theme bug can raise the impact
An inactive theme may still be loaded when WordPress generates a preview in the Customizer. In its proof of concept, pwn.ai used the Mobile Repair Zone theme, which contained a separate background handler flaw. The handler accepted a web address from a request, downloaded a package and ran its code without checking the visitor’s permission or a security token.
When combined with the forced installation, that theme-level weakness allowed attacker-controlled code to run on the server. The distinction matters: updating WordPress core closes the demonstrated Click2Shell path regardless of the theme in use, while the critical result shown by researchers required the second vulnerability.
Patch status and operational response
The September 17 security release addresses affected versions from WordPress 6.0 through releases immediately before the fix, with fixes delivered to supported branches back to 4.7. Site owners should install WordPress 7.1.1 or the matching security update for their branch; sites configured for automatic updates will receive the update automatically.
WordPress and pwn.ai did not provide a separate workaround for organisations unable to patch immediately. The attack requires a logged-in administrator to open the malicious link, and there is no indication that Click2Shell has been exploited in real attacks. The broader WordPress exposure is illustrated by mass attacks involving WordPress and Joomla infrastructure, which documents mass attacks involving WordPress and Joomla infrastructure.
For businesses, the immediate action is to verify that core security updates have reached every WordPress instance, including less visible sites and supported legacy branches. Administrators should also treat unsolicited theme-related links as untrusted until patch deployment is confirmed.