


Active Exploitation Targets WSO2 JWT Authentication Bypass
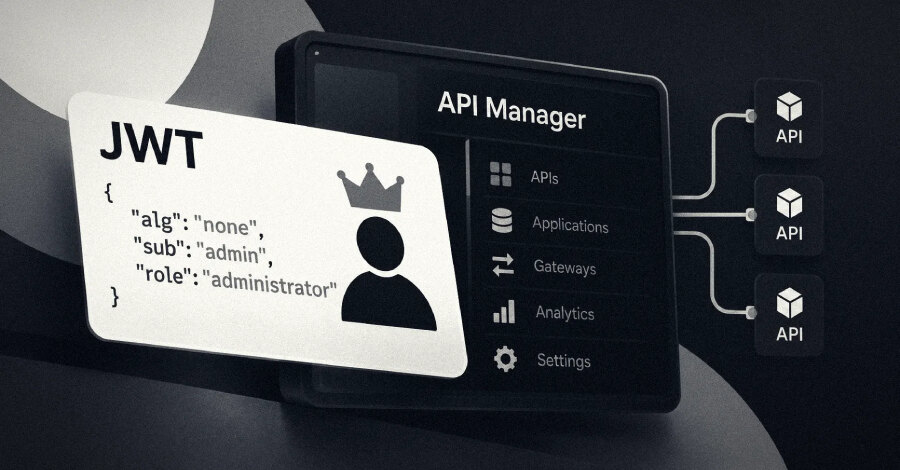
Forged administrator tokens seen in WSO2 attacks
Security researchers at watchTowr have observed active exploitation attempts against CVE-2026-5430, a critical JWT authentication bypass in WSO2 API products. The flaw carries a CVSS score of 9.8 out of 10, while watchTowr described it as a CVSS 10.0 issue because of its potential impact. Its honeypot network captured JWTs carrying baked-in administrator privileges on September 13, 2026.
Hacktron Team discovered and reported the vulnerability. WSO2 disclosed it in an advisory in May 2026, warning that JWT authentication could be bypassed when a token is signed with an unsupported algorithm. Successful exploitation can provide unauthorized access, including compromise of administrative accounts and full account takeover.
Why the flaw can expose API environments
The issue is an improper verification of a cryptographic signature. Yordan Ganchev, principal threat intelligence specialist at watchTowr, said the affected service accepts JWTs signed with algorithms it does not support and then approves them. That behaviour allows an attacker to present a forged token that the service should have rejected.
In the activity observed by watchTowr, the forged JWT is suspected of being used to reach every API backend endpoint and obtain credentials, consumer keys and secrets associated with each registered application. Because these products intercept API requests headed to internal systems, access could also create an opportunity to capture sensitive data in transit and interact with internal services.
Affected products and available fixes
Affected versions are WSO2 API Manager 4.1.0 through 4.6.0; WSO2 API Control Plane 4.5.0 and 4.6.0; WSO2 Traffic Manager 4.5.0 and 4.6.0; and WSO2 Universal Gateway 4.5.0 and 4.6.0.
For community users, WSO2 has made fixes available through pull requests 13752 in carbon-apimgt and 14167 in product-apim. Support Subscription holders can obtain fixes at update level 22 for API Control Plane 4.6.0 and 58 for 4.5.0; update levels 21, 57, 72, 108, 197 and 257 for API Manager versions 4.6.0 to 4.1.0 respectively.
Traffic Manager is fixed at update level 21 for 4.6.0 and 56 for 4.5.0, while Universal Gateway is fixed at update level 21 for 4.6.0 and 57 for 4.5.0.
Business implication
Organizations using affected WSO2 deployments should apply the relevant fix or supported update level as soon as possible, then review administrative access and the API credentials, consumer keys and secrets that could be exposed through a compromised gateway.