


Xen grant copy flaws break virtual machine memory isolation
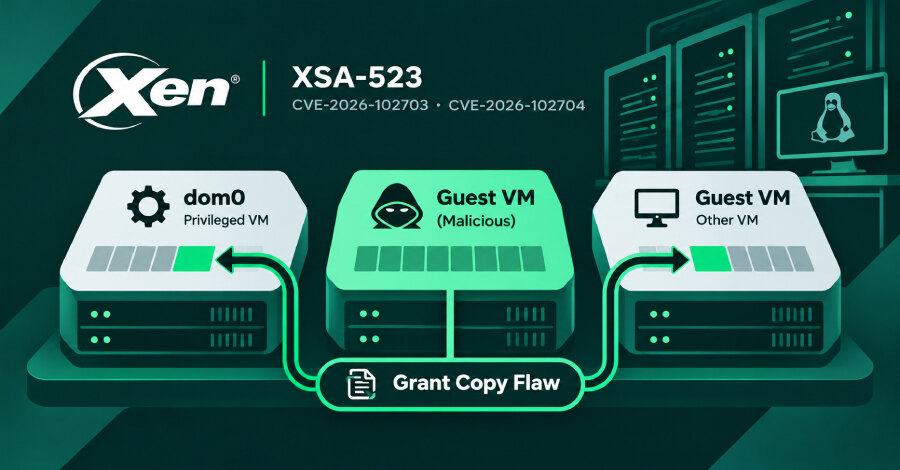
The Xen Project has released patches for two vulnerabilities that allow a malicious guest virtual machine to read and write memory belonging to other VMs on the same host, including dom0. The issues are tracked as CVE-2026-102703 and CVE-2026-102704 in advisory XSA-523, and affect Xen versions 4.6 and later.
Dom0 is Xen’s privileged management VM and normally has full authority over the host and its guests. Access to its memory therefore makes these flaws especially serious in shared or multi-workload environments. Xen said there is no known mitigation; applying the available fixes is the prescribed response.
Grant copy permission checks can be reused incorrectly
The defects are in grant copy, an operation used by Xen to transfer data between VMs. Guests specify which of their memory pages may be used by other guests, and Xen is supposed to validate the relevant permissions before a copy is performed.
For efficiency, Xen can reuse permission checks across a batch of copies involving the same memory page. In some circumstances, however, it failed to perform a fresh check when required. That gap can allow a malicious guest to access memory outside the pages it is permitted to use.
The Xen Project credited Anthropic with finding the issues using its Claude model. Stephan Lipp of Ada Logics validated the finding, while the CodeAnt AI Security Research Team independently reported the same problem.
Patch status varies across Xen-based platforms
Patches are available in the Xen advisory for xen-unstable through Xen 4.19.x and for the maintained 4.17.x to 4.18.x branches. No patch is provided for Xen 4.6 through 4.16; security support for Xen 4.16 ended on December 2, 2024. Releases 4.5 and earlier are not affected.
XCP-ng 8.3 issued xen-4.17.7-4.2.xcpng8.3 on November 3 and requires hosts to be rebooted after updating. Vates, the company behind XCP-ng, rated the issue Critical and warned that a single compromised guest could escape isolation and take over the host.
Qubes OS said every supported release and configuration is affected. Its fix for the supported Qubes 4.3 release is Xen package 4.19.6-3 in dom0. Administrators must restart dom0; users of Anti Evil Maid must also reseal their secret passphrase because the updated Xen binaries alter PCR18 and PCR19.
Debian’s tracker listed Xen packages in bookworm, trixie and forky as vulnerable on November 4, while sid was marked fixed. XSA-523 is distinct from XSA-500, the grant copy issue disclosed on July 28, and needs its own patches.
Operational priority for virtualisation teams
Teams running Xen should identify every host and dependent platform, determine the installed Xen branch, and deploy the vendor’s XSA-523 update where one exists. They should schedule the required reboots and give particular attention to unsupported 4.6–4.16 installations, where the practical business implication is an urgent decision on migration or compensating workload isolation because no vendor patch is published.