


Yoba malware hides crypto miners in fake ChatGPT and Claude apps
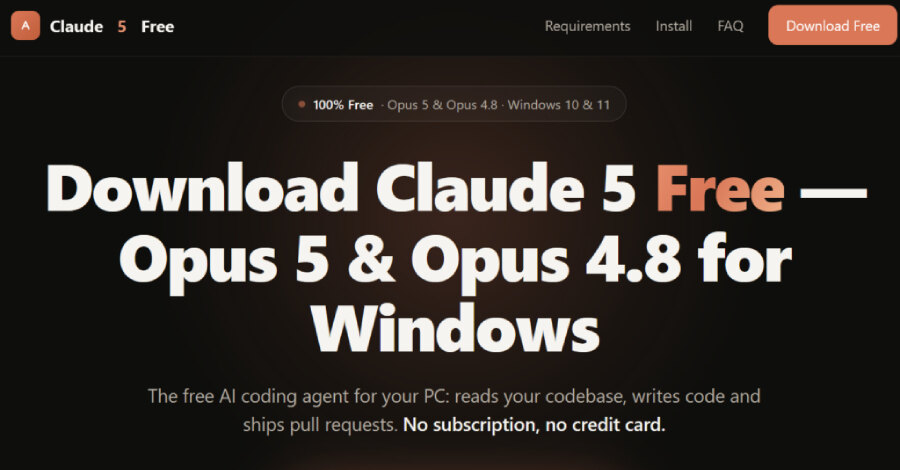
Check Point Research has identified a malware campaign called Yoba that distributes cryptocurrency miners through fake desktop applications branded as Anthropic Claude and OpenAI ChatGPT. The attackers created GitHub projects and GitHub.io pages promoting purported products including GPT-5.6 Sol, GPT-6 Astra and Claude Opus, then offered ZIP archives containing malware alongside legitimate signed executables.
Each archive includes Setup.exe, described as a legitimate signed OpenAI Codex or Claude executable, and a malicious winmm.dll. The arrangement abuses DLL sideloading: when the trusted executable runs, it loads the attacker-controlled library rather than requiring the malicious code to launch directly. Check Point said the campaign uses the credibility of prominent AI software names and GitHub-hosted projects to make the downloads appear legitimate.
Signed binaries initiate a multi-stage chain
The first DLL, dubbed YobaDropper, checks the hash of its host executable's basename and only proceeds when it is launched as Setup.exe. This condition frustrates analysis when the DLL is executed independently in a sandbox. The dropper also uses repeated Sleep(5500) calls—200,000 iterations in total, equivalent to 12.73 days—and avoids systems using keyboard layouts associated with Russia, Belarus, Tajikistan, Armenia, Azerbaijan, Georgia, Kazakhstan, Kyrgyzstan, Turkmenistan and Uzbekistan, as well as Tatar.
YobaDropper then starts another sideloading sequence using wmpdmc.exe and ampdui.dll. It copies wmpdmc.exe from the system32 directory into a ProgramData subdirectory named WMProcess, decrypts an embedded payload and places it there as wmpdui.dll. A scheduled task launches the legitimate executable, giving the malicious payload a persistence mechanism.
Telegram seed and DNS-over-HTTPS command retrieval
The next component, YobaLoader, applies a similar host check and requires execution under wmpdmc.exe. It downloads an image from a Telegram channel, takes its final 50 bytes as a seed, and generates a domain in the form adjective-noun-verb-digit.dedyn.io. It then queries Google's DNS-over-HTTPS API for a Base64-encoded command stored in a DNS TXT record and decrypts the response to obtain the address of the next payload.
That payload is injected into svchost.exe and executes an XMRig cryptocurrency miner. This use of a common DoH service and mainstream file-hosting infrastructure is intended to make command-and-control activity harder to distinguish from normal traffic and to bypass some passive DNS and gateway controls. The broader risk around trusted AI brands is also illustrated by OpenAI compromise through Claude attack path examining how OpenAI was compromised with Claude, where familiar AI services feature in an unexpected attack path.
Repository credibility is part of the delivery mechanism
Check Point found that the repositories used different uploader email addresses and apparent operating time zones, an inconsistency it assessed as an effort to hide the operator's true location. The first repository appears to have been created around July 2026, while malicious releases were uploaded near the end of August. Researchers also observed that early YobaLoader versions excluded only Russia and included extensive anti-debugging and anti-virtual-machine checks that were removed in later versions.
For businesses, the practical response is to treat AI-branded desktop downloads from code-sharing platforms as untrusted unless they are obtained through verified vendor distribution channels. Endpoint teams should investigate unsigned or unexpected DLLs placed beside signed executables, new scheduled tasks that launch those binaries, unusual DNS-over-HTTPS activity and process injection into svchost.exe.